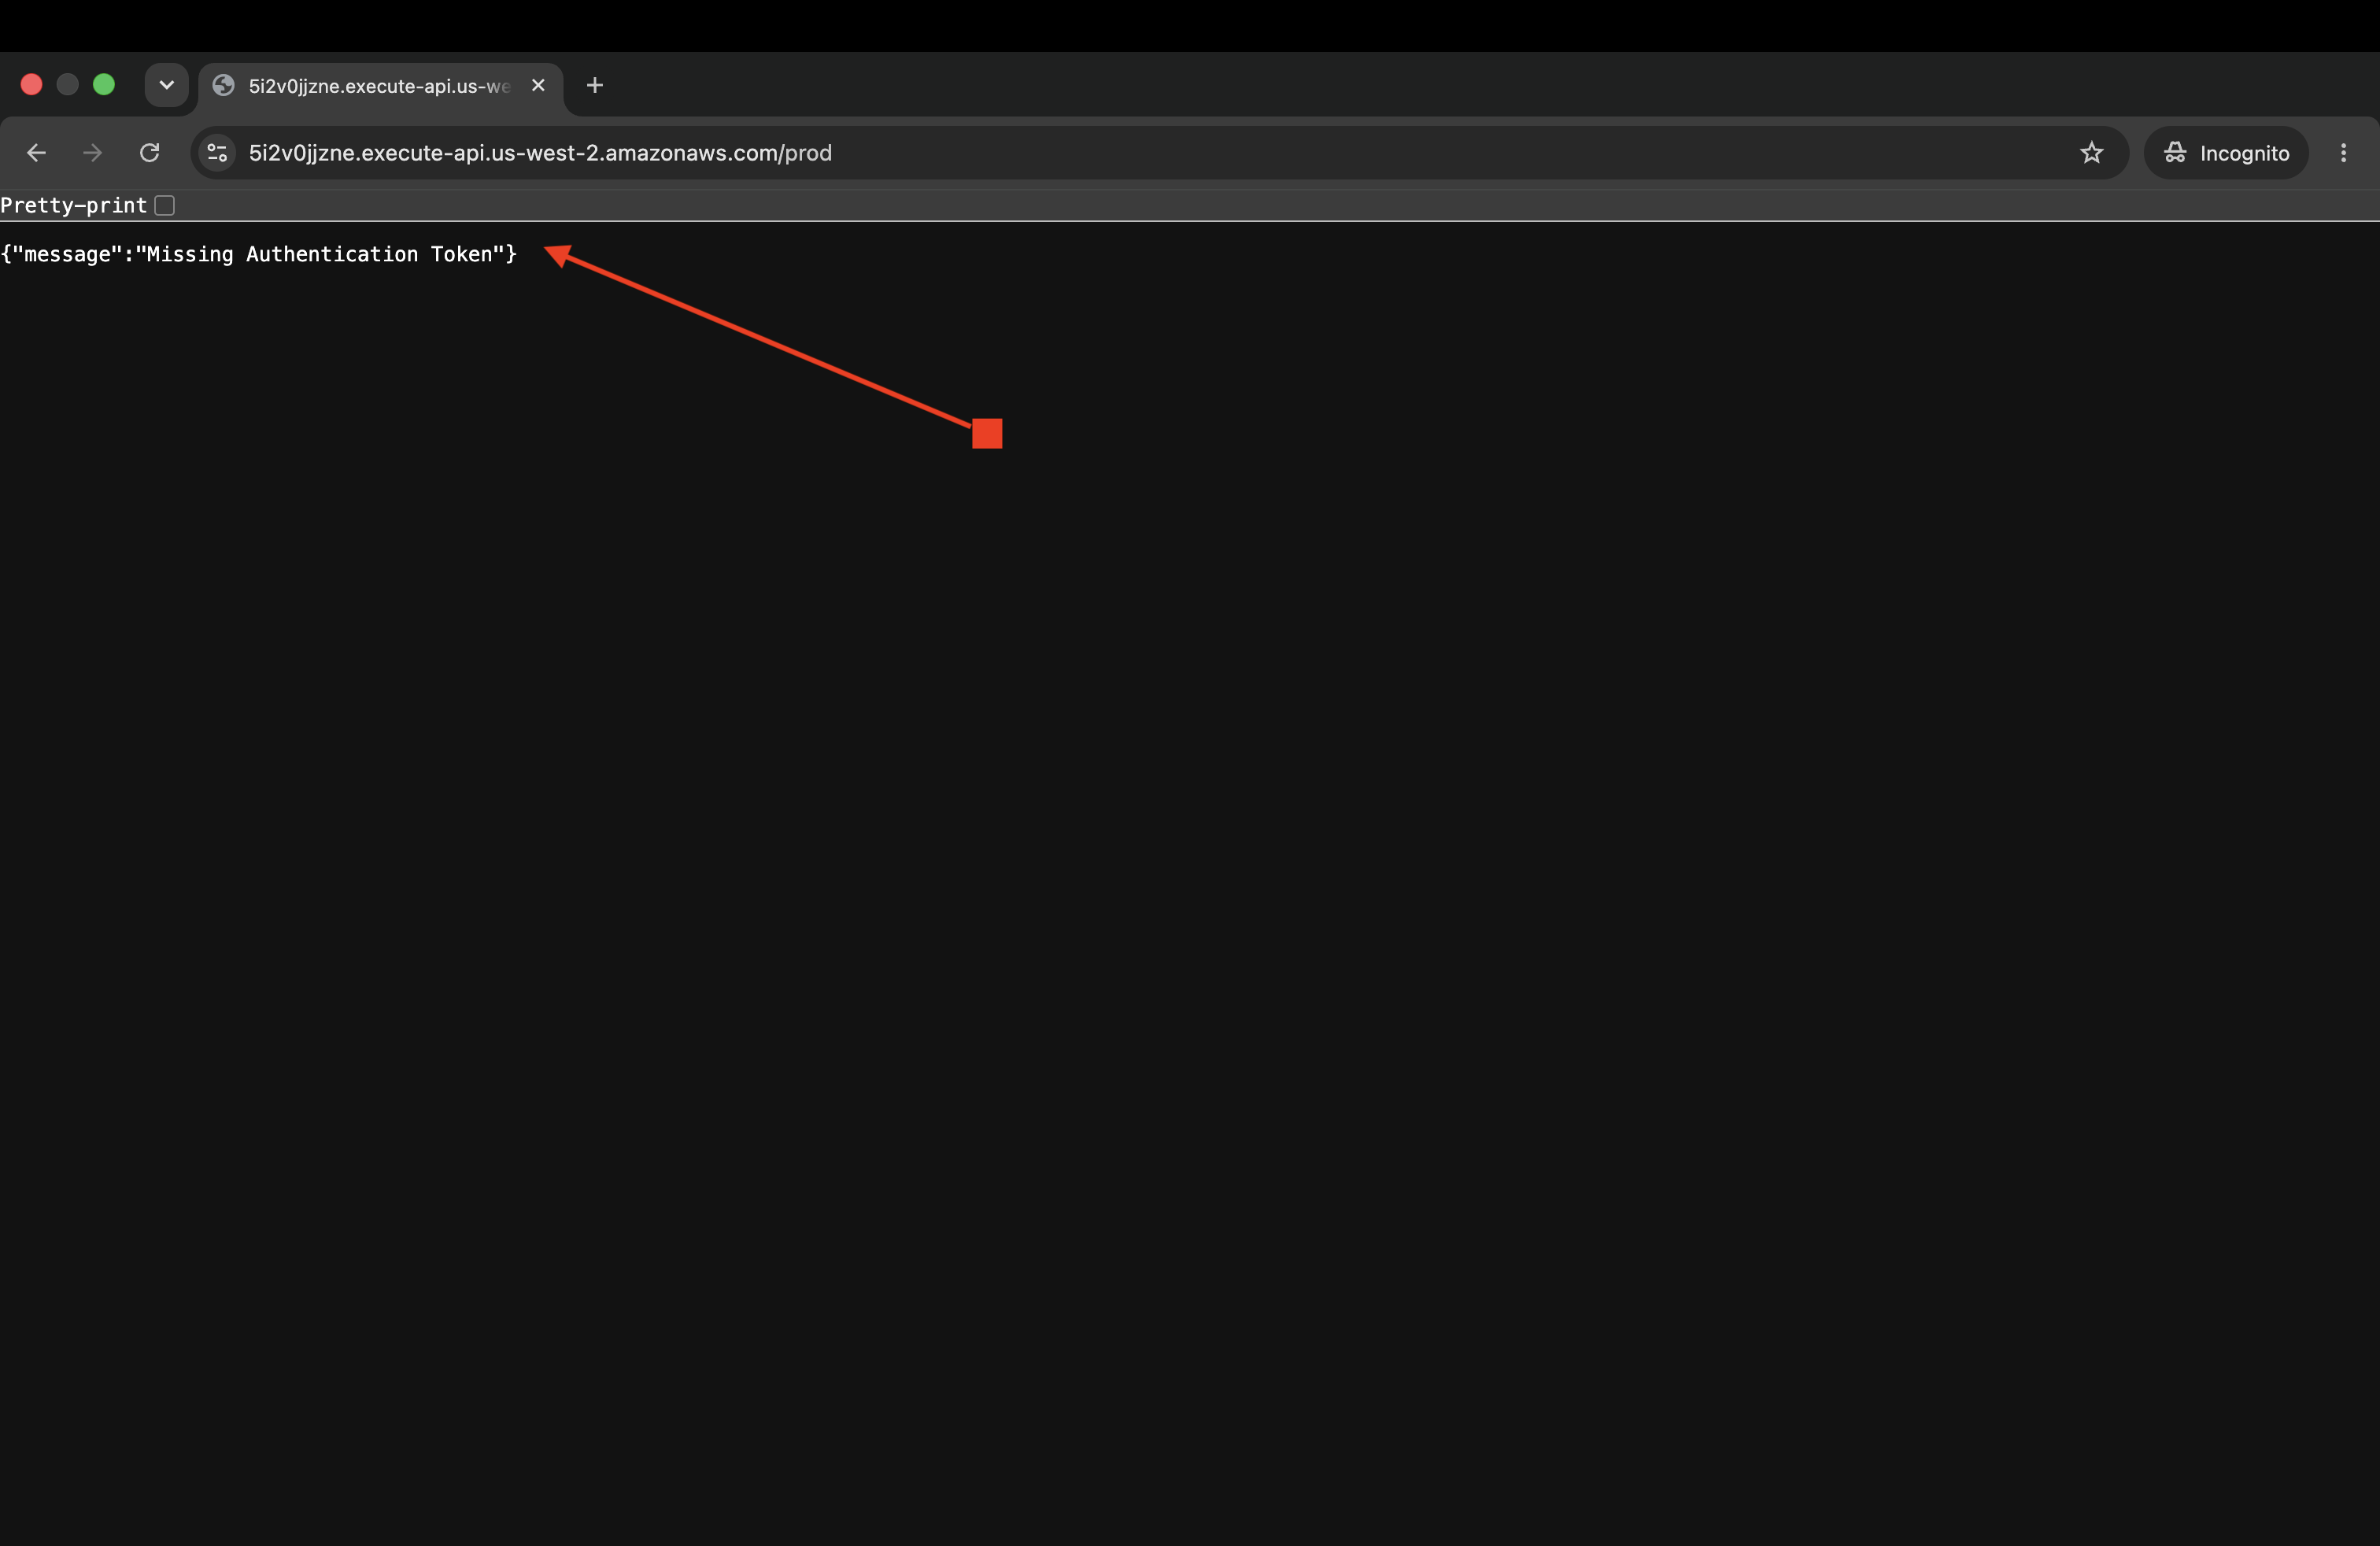
1. Portal Landing & Login Gate:
Initial entry point at https://client.e5cloud.com enforcing perimeter security policies.
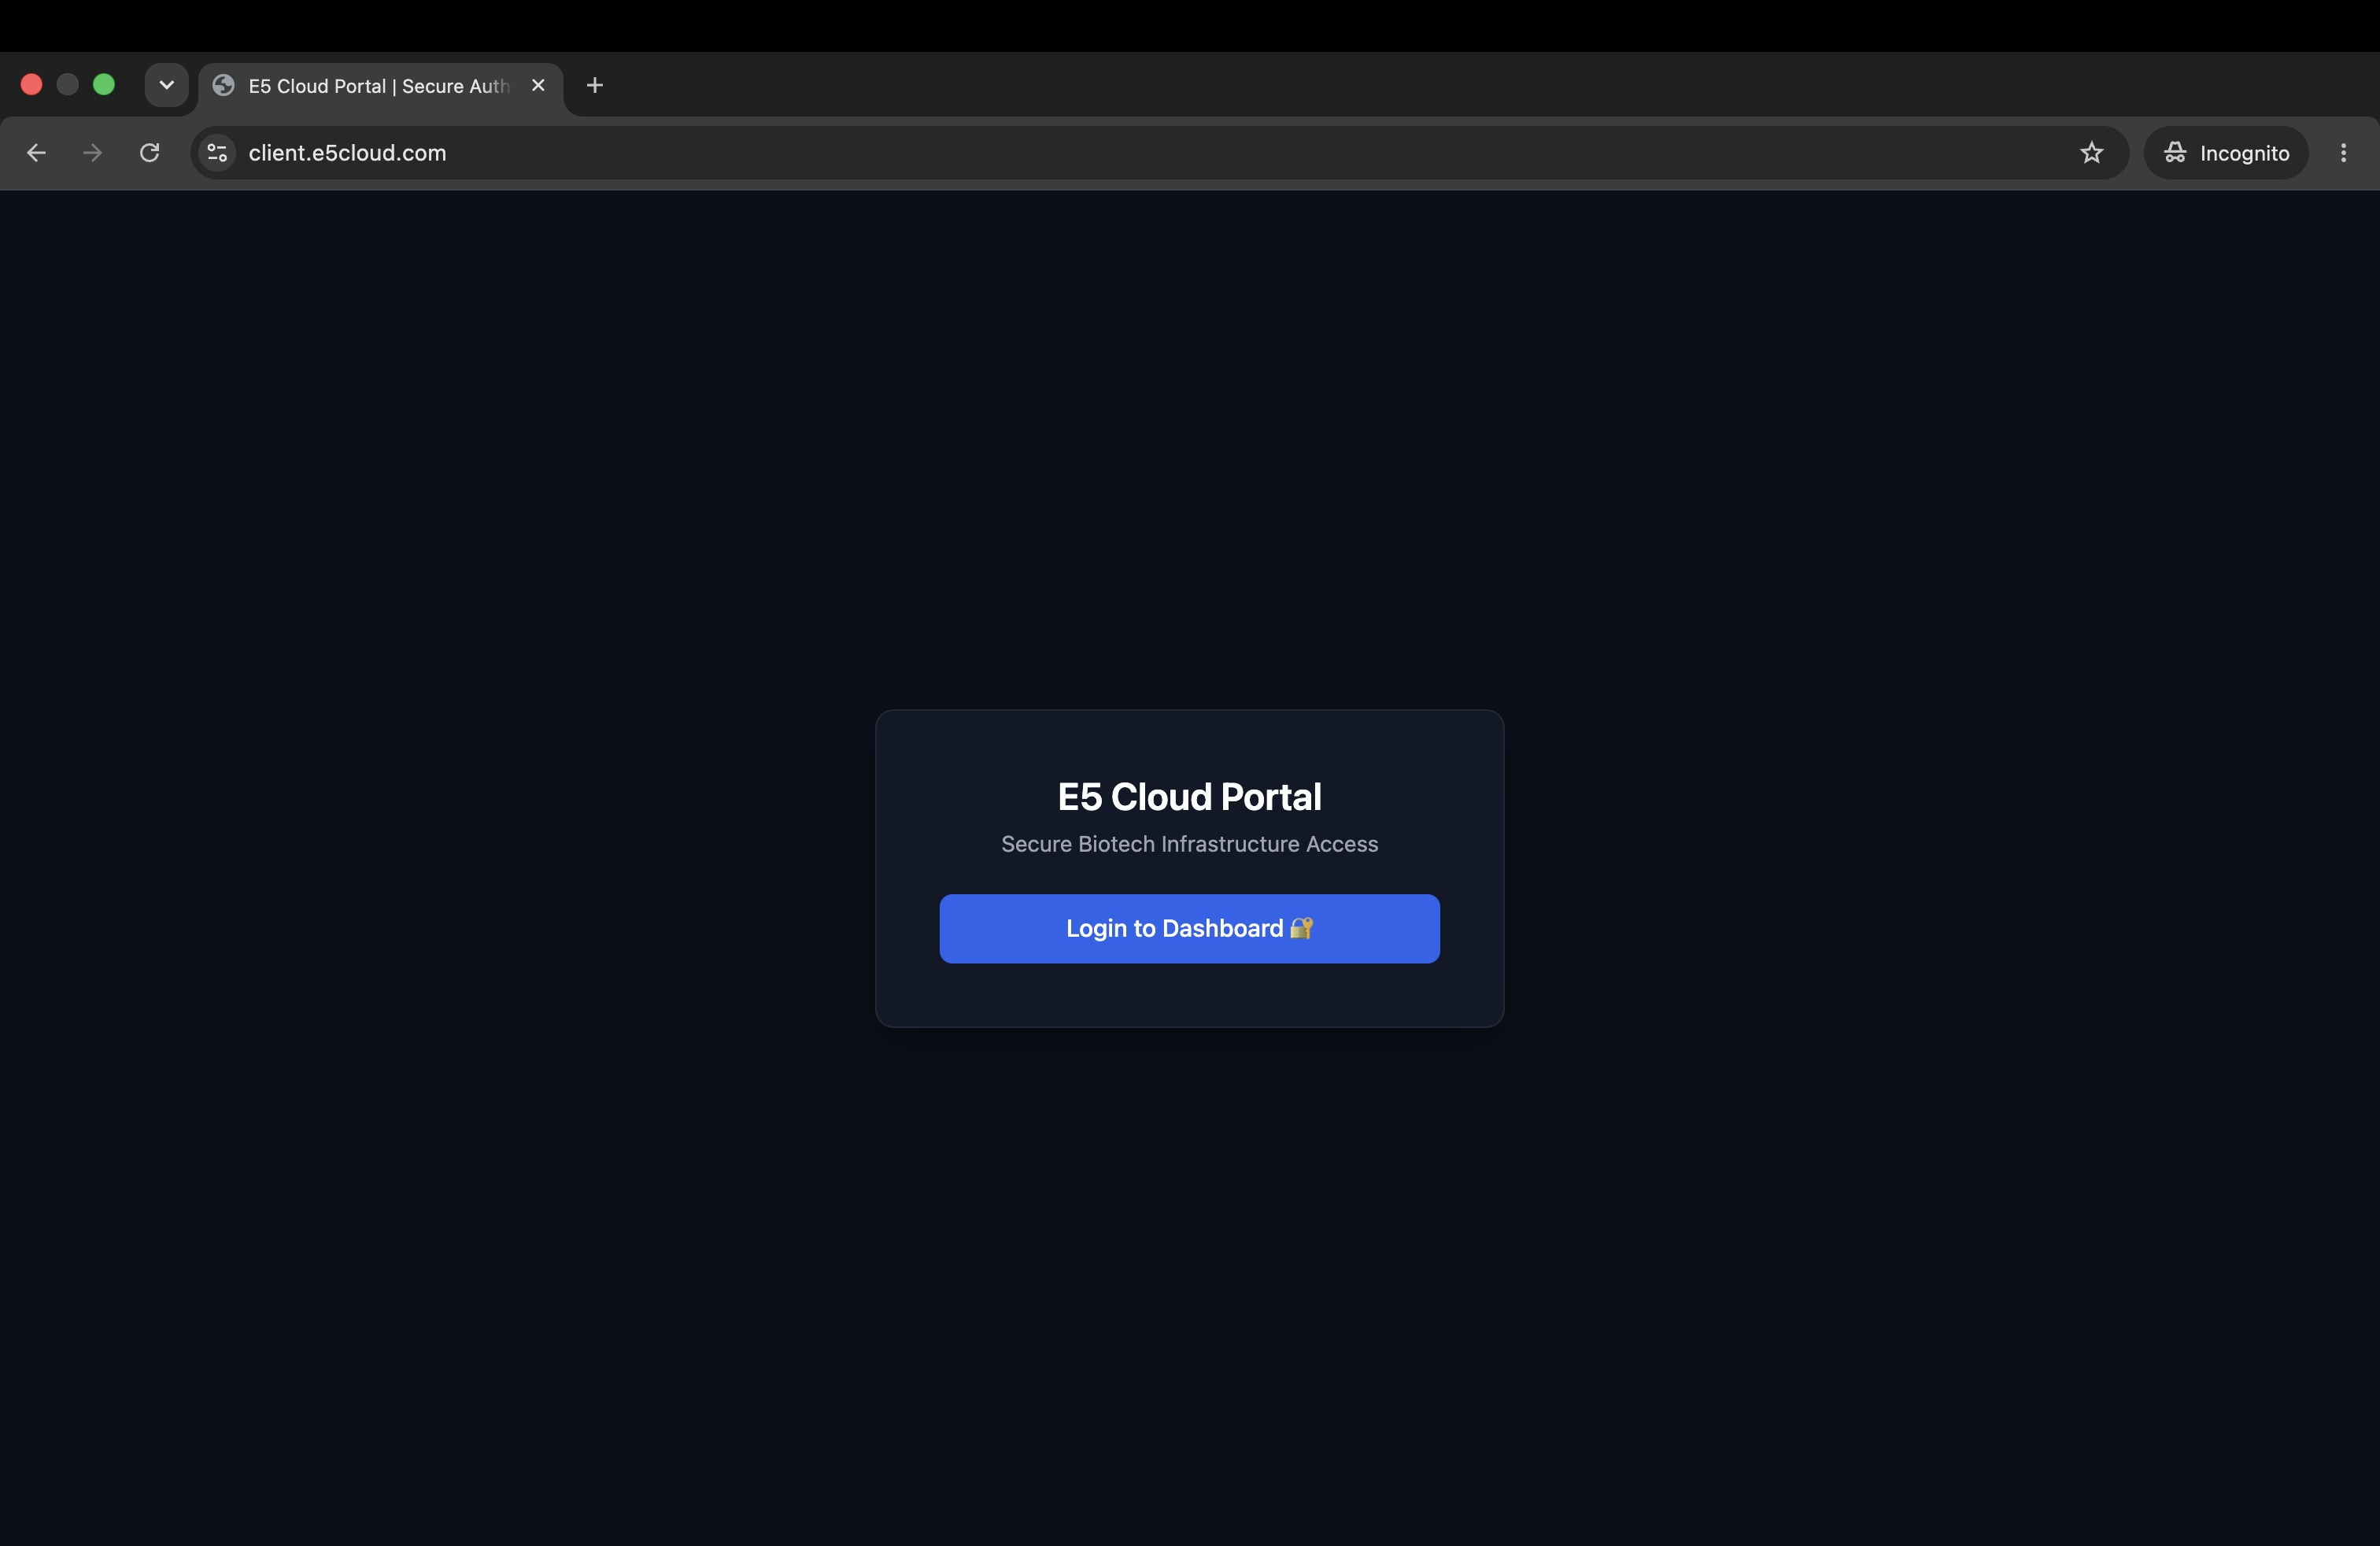
2. Amazon Cognito Hosted UI Challenge:
Managed credential collection and secure IAM token exchange sequence via Amazon Cognito.
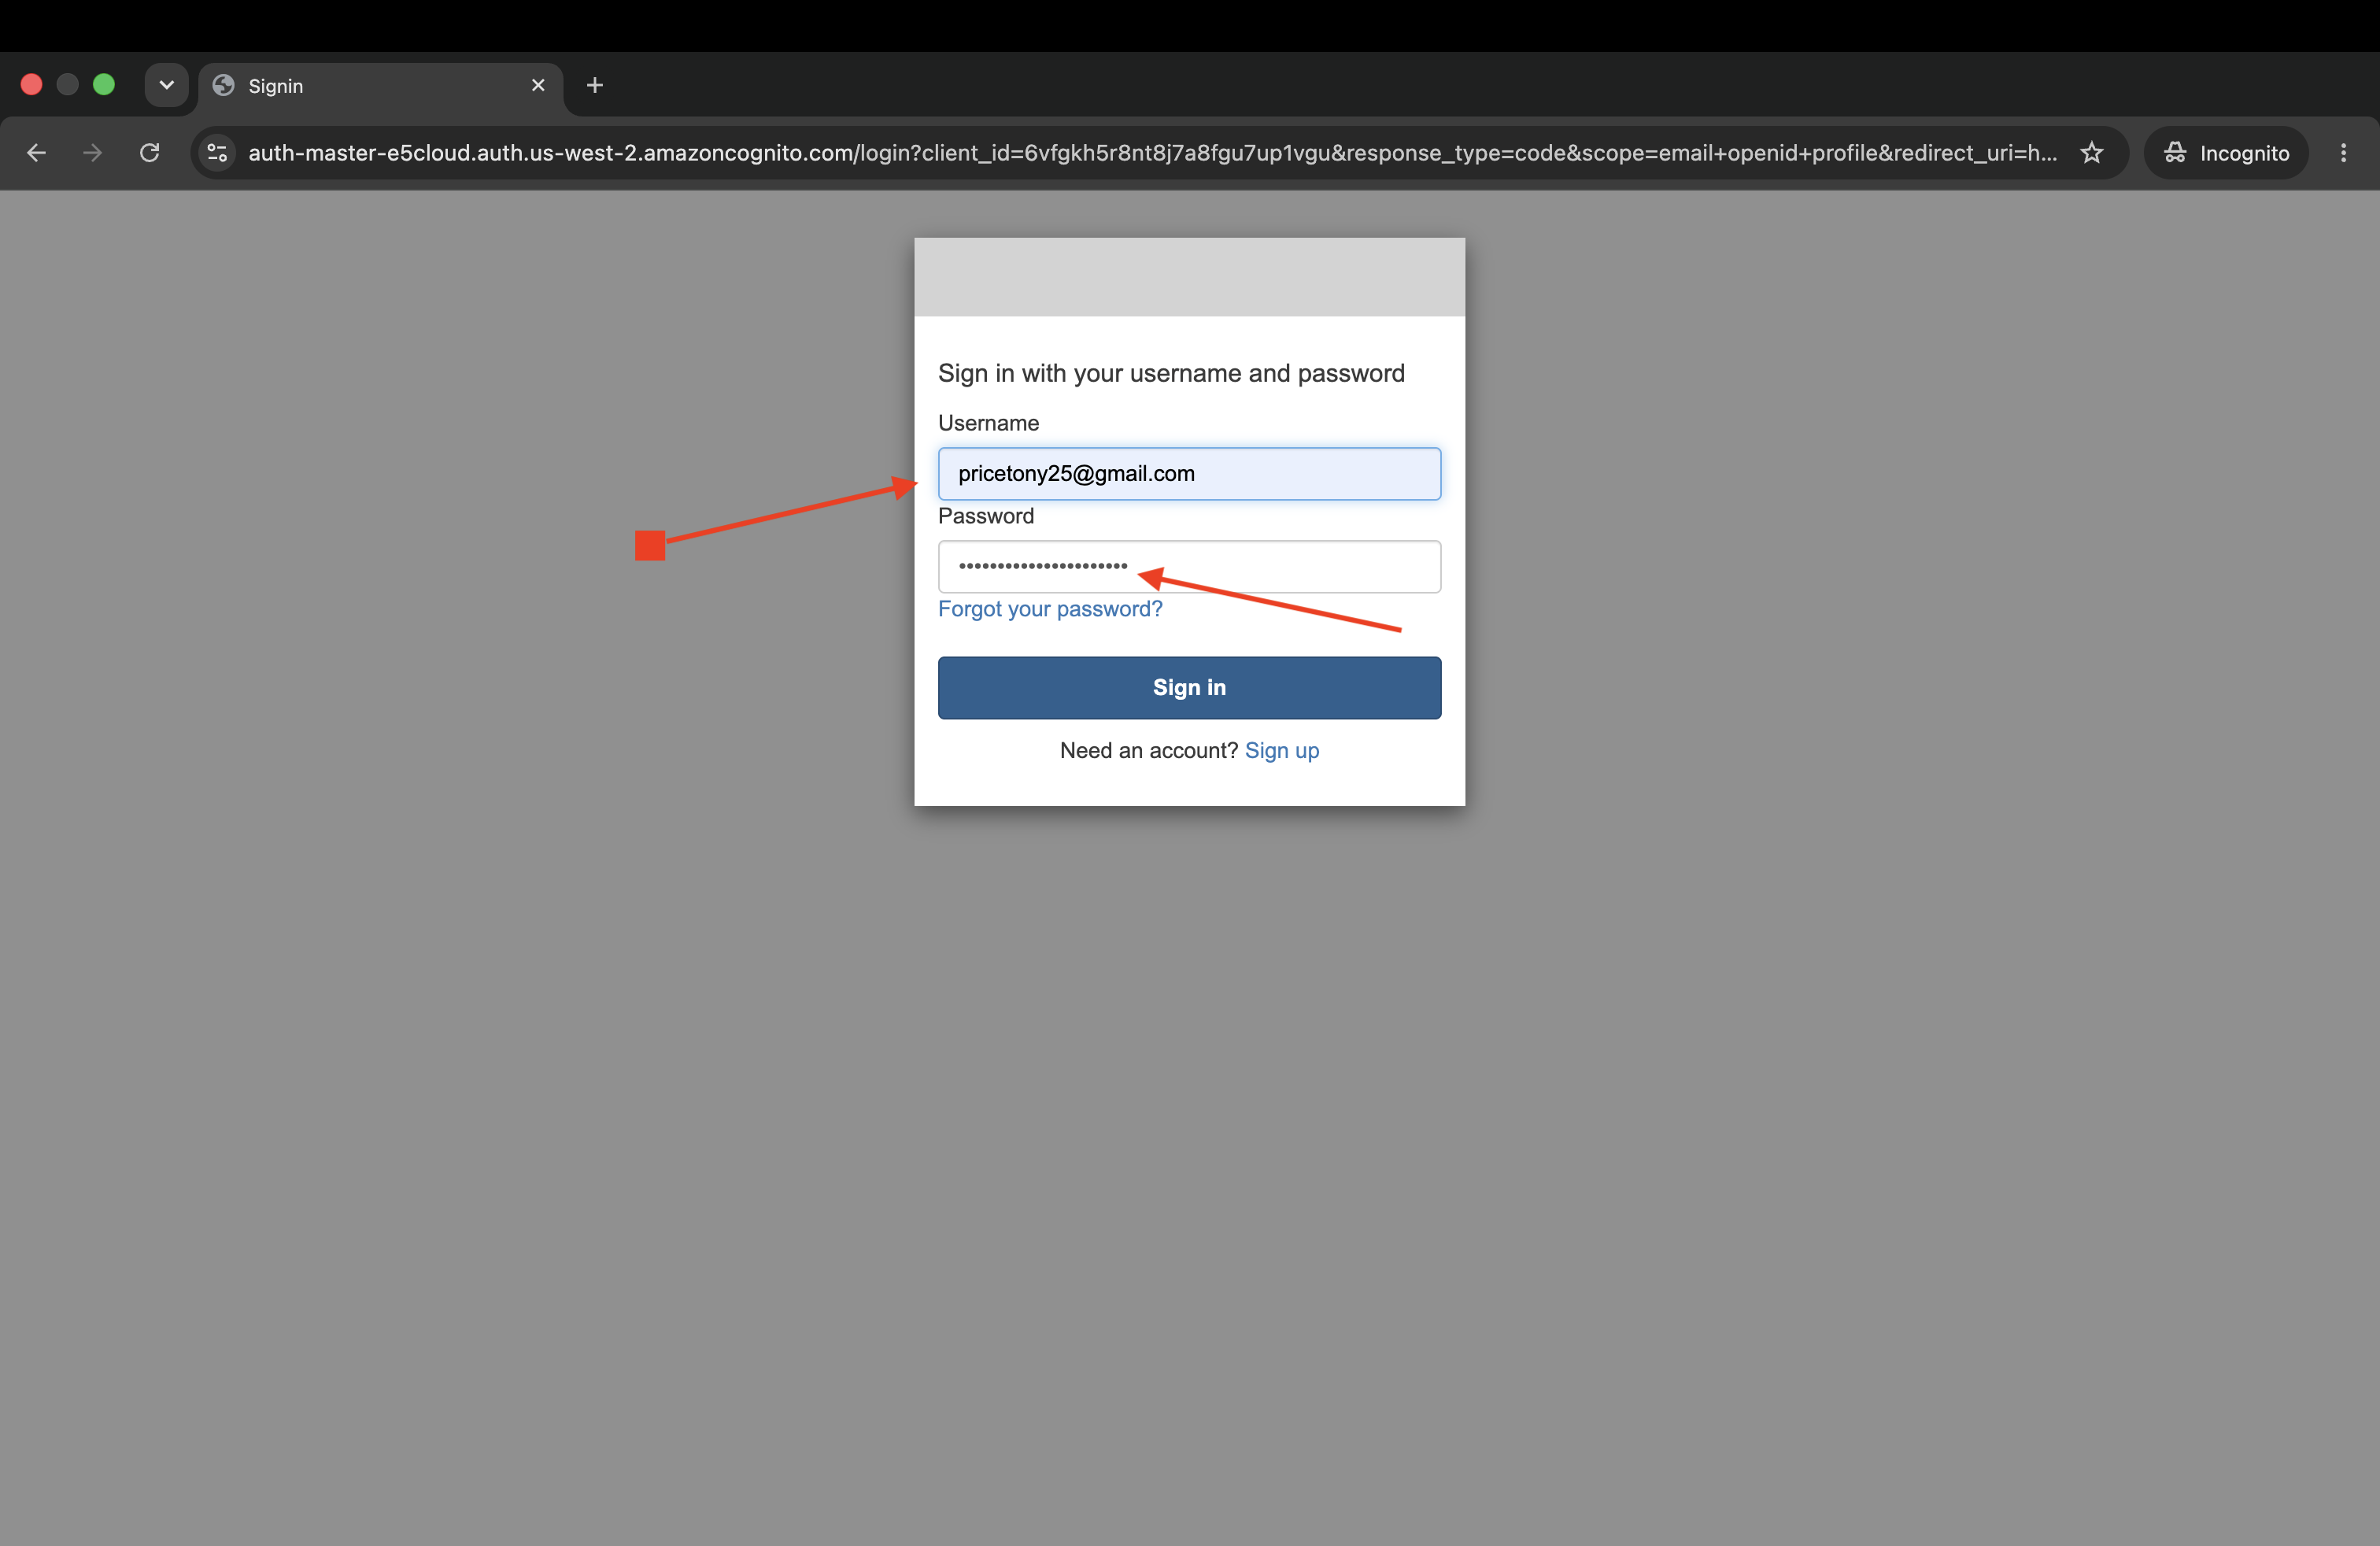
3. Executive Command Center Dashboard:
Centralized administrative console at https://client.e5cloud.com/admin providing workspace controls, consumption gauges, and vault navigation.
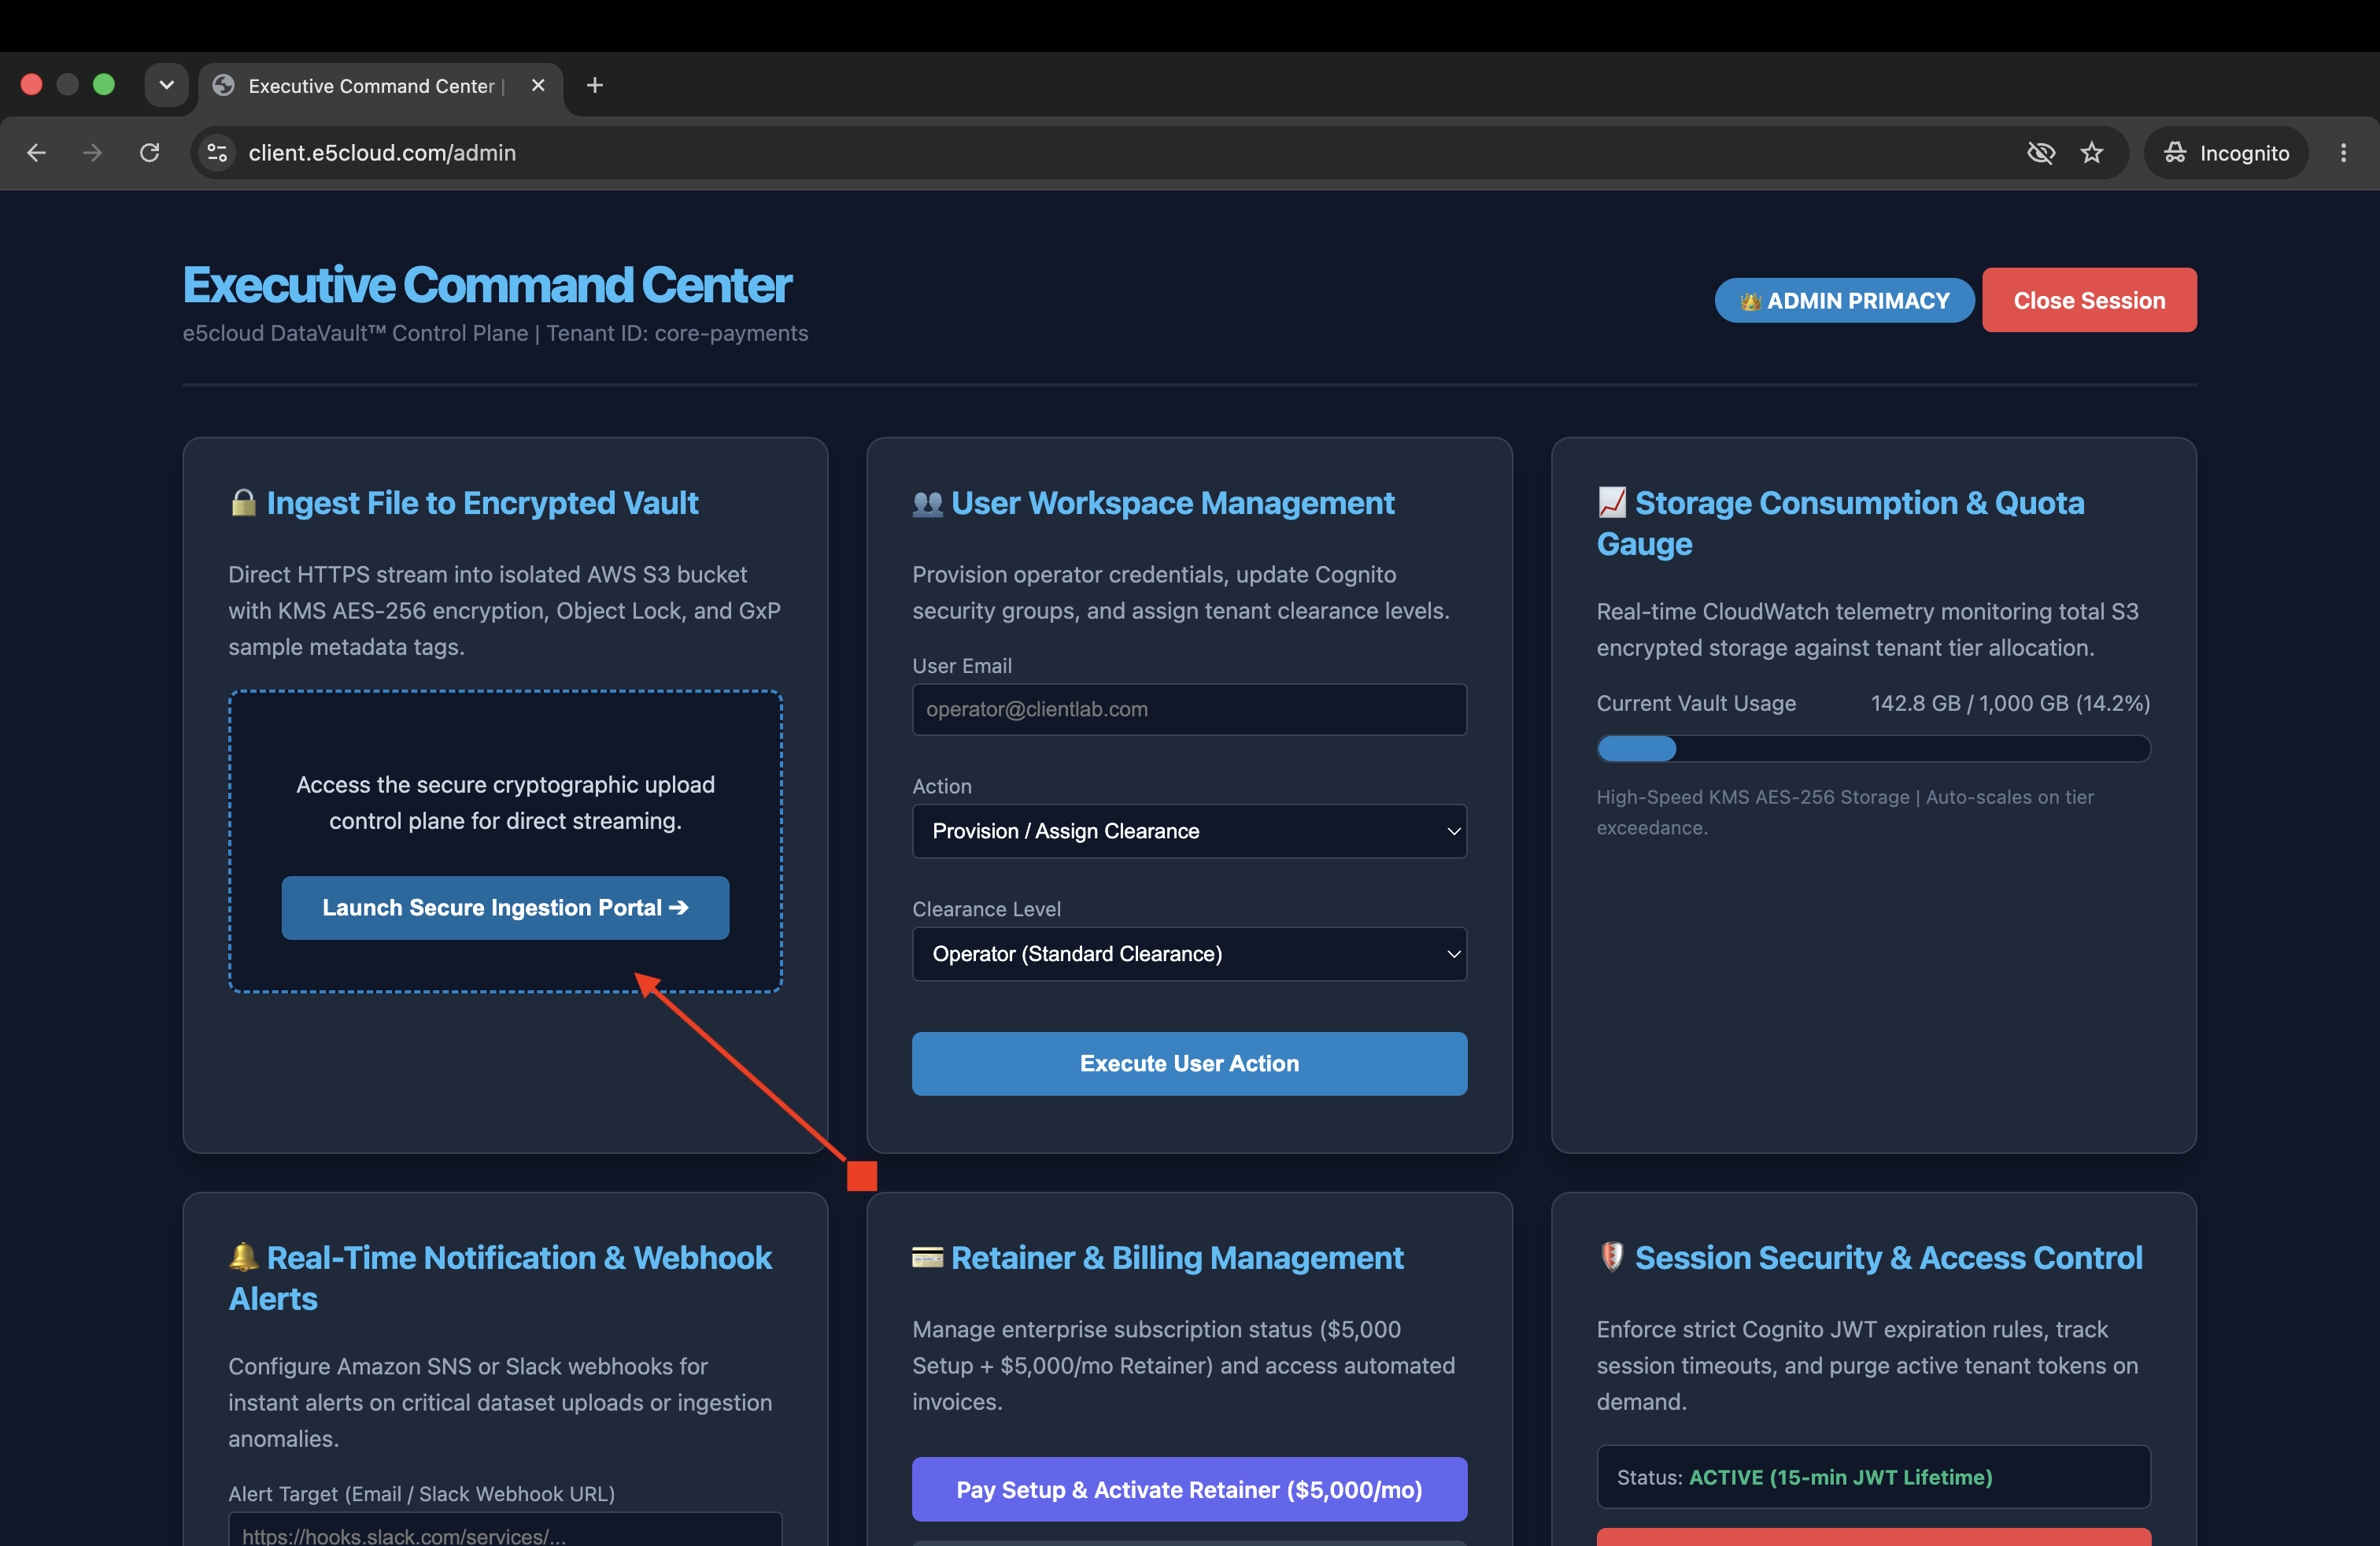
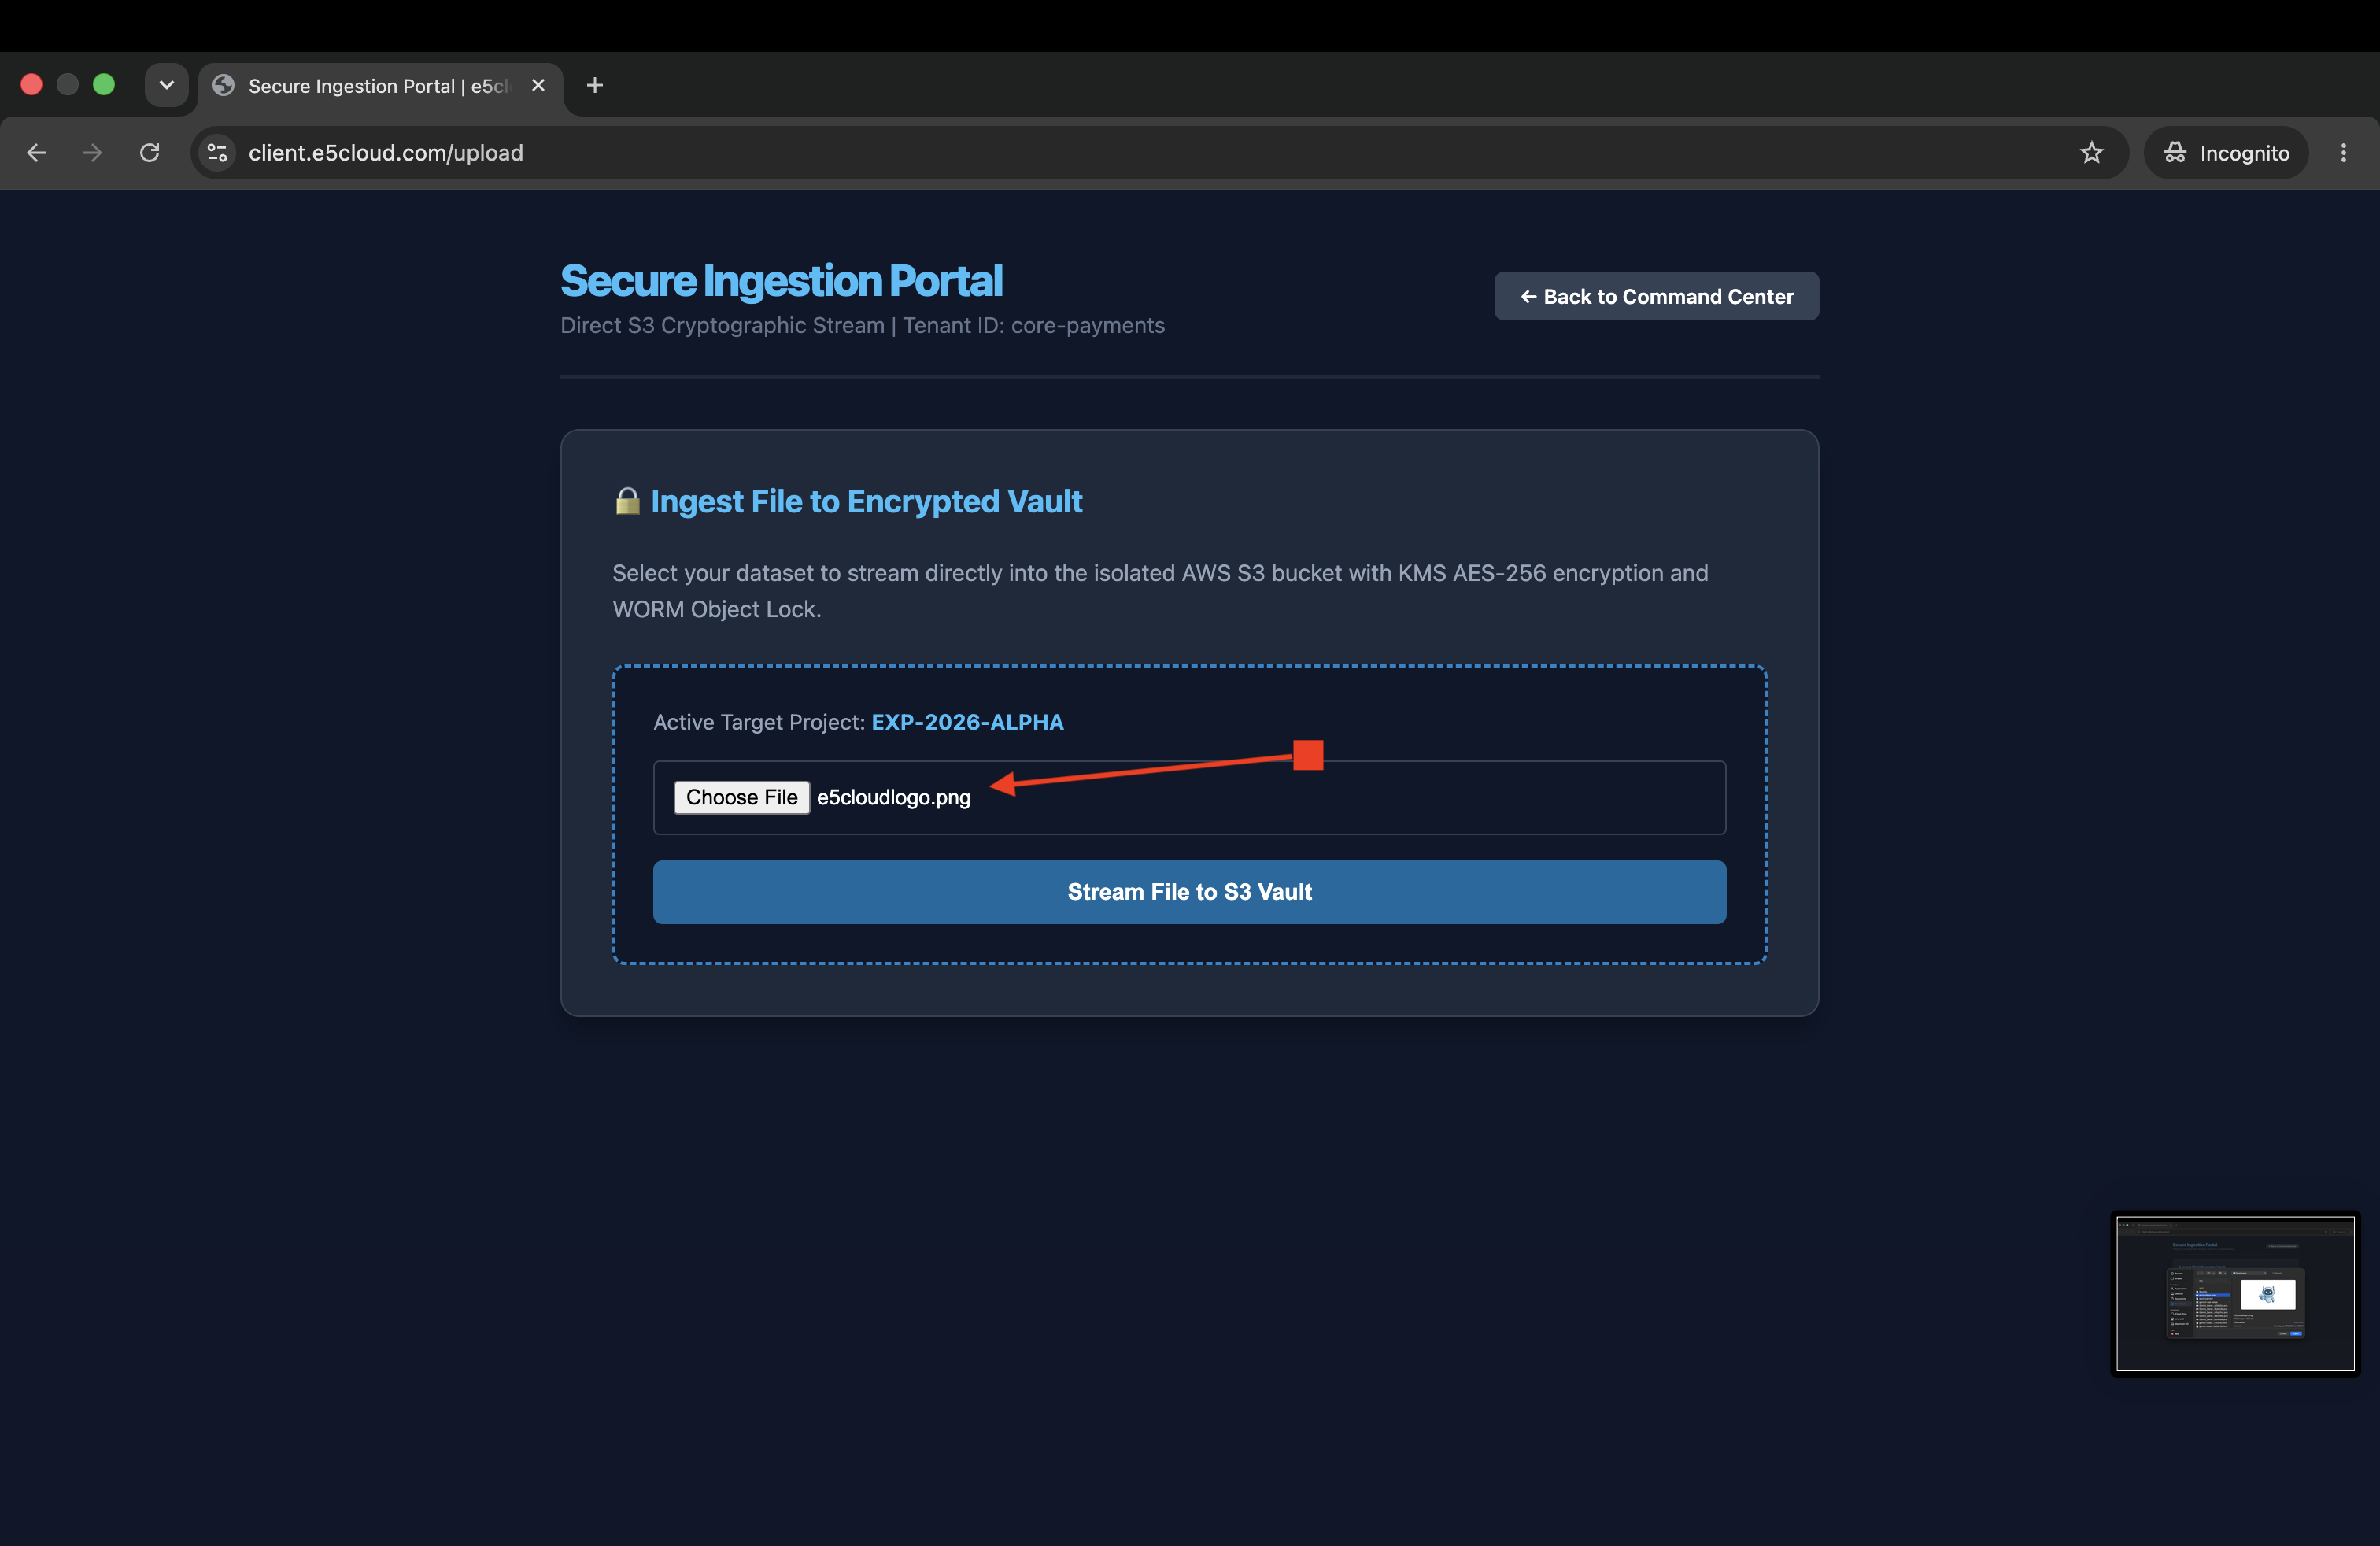
4. Secure Ingestion Portal (File Selection):
Cryptographic streaming interface targeted to EXP-2026-ALPHA with AES-256 and WORM enforcement.
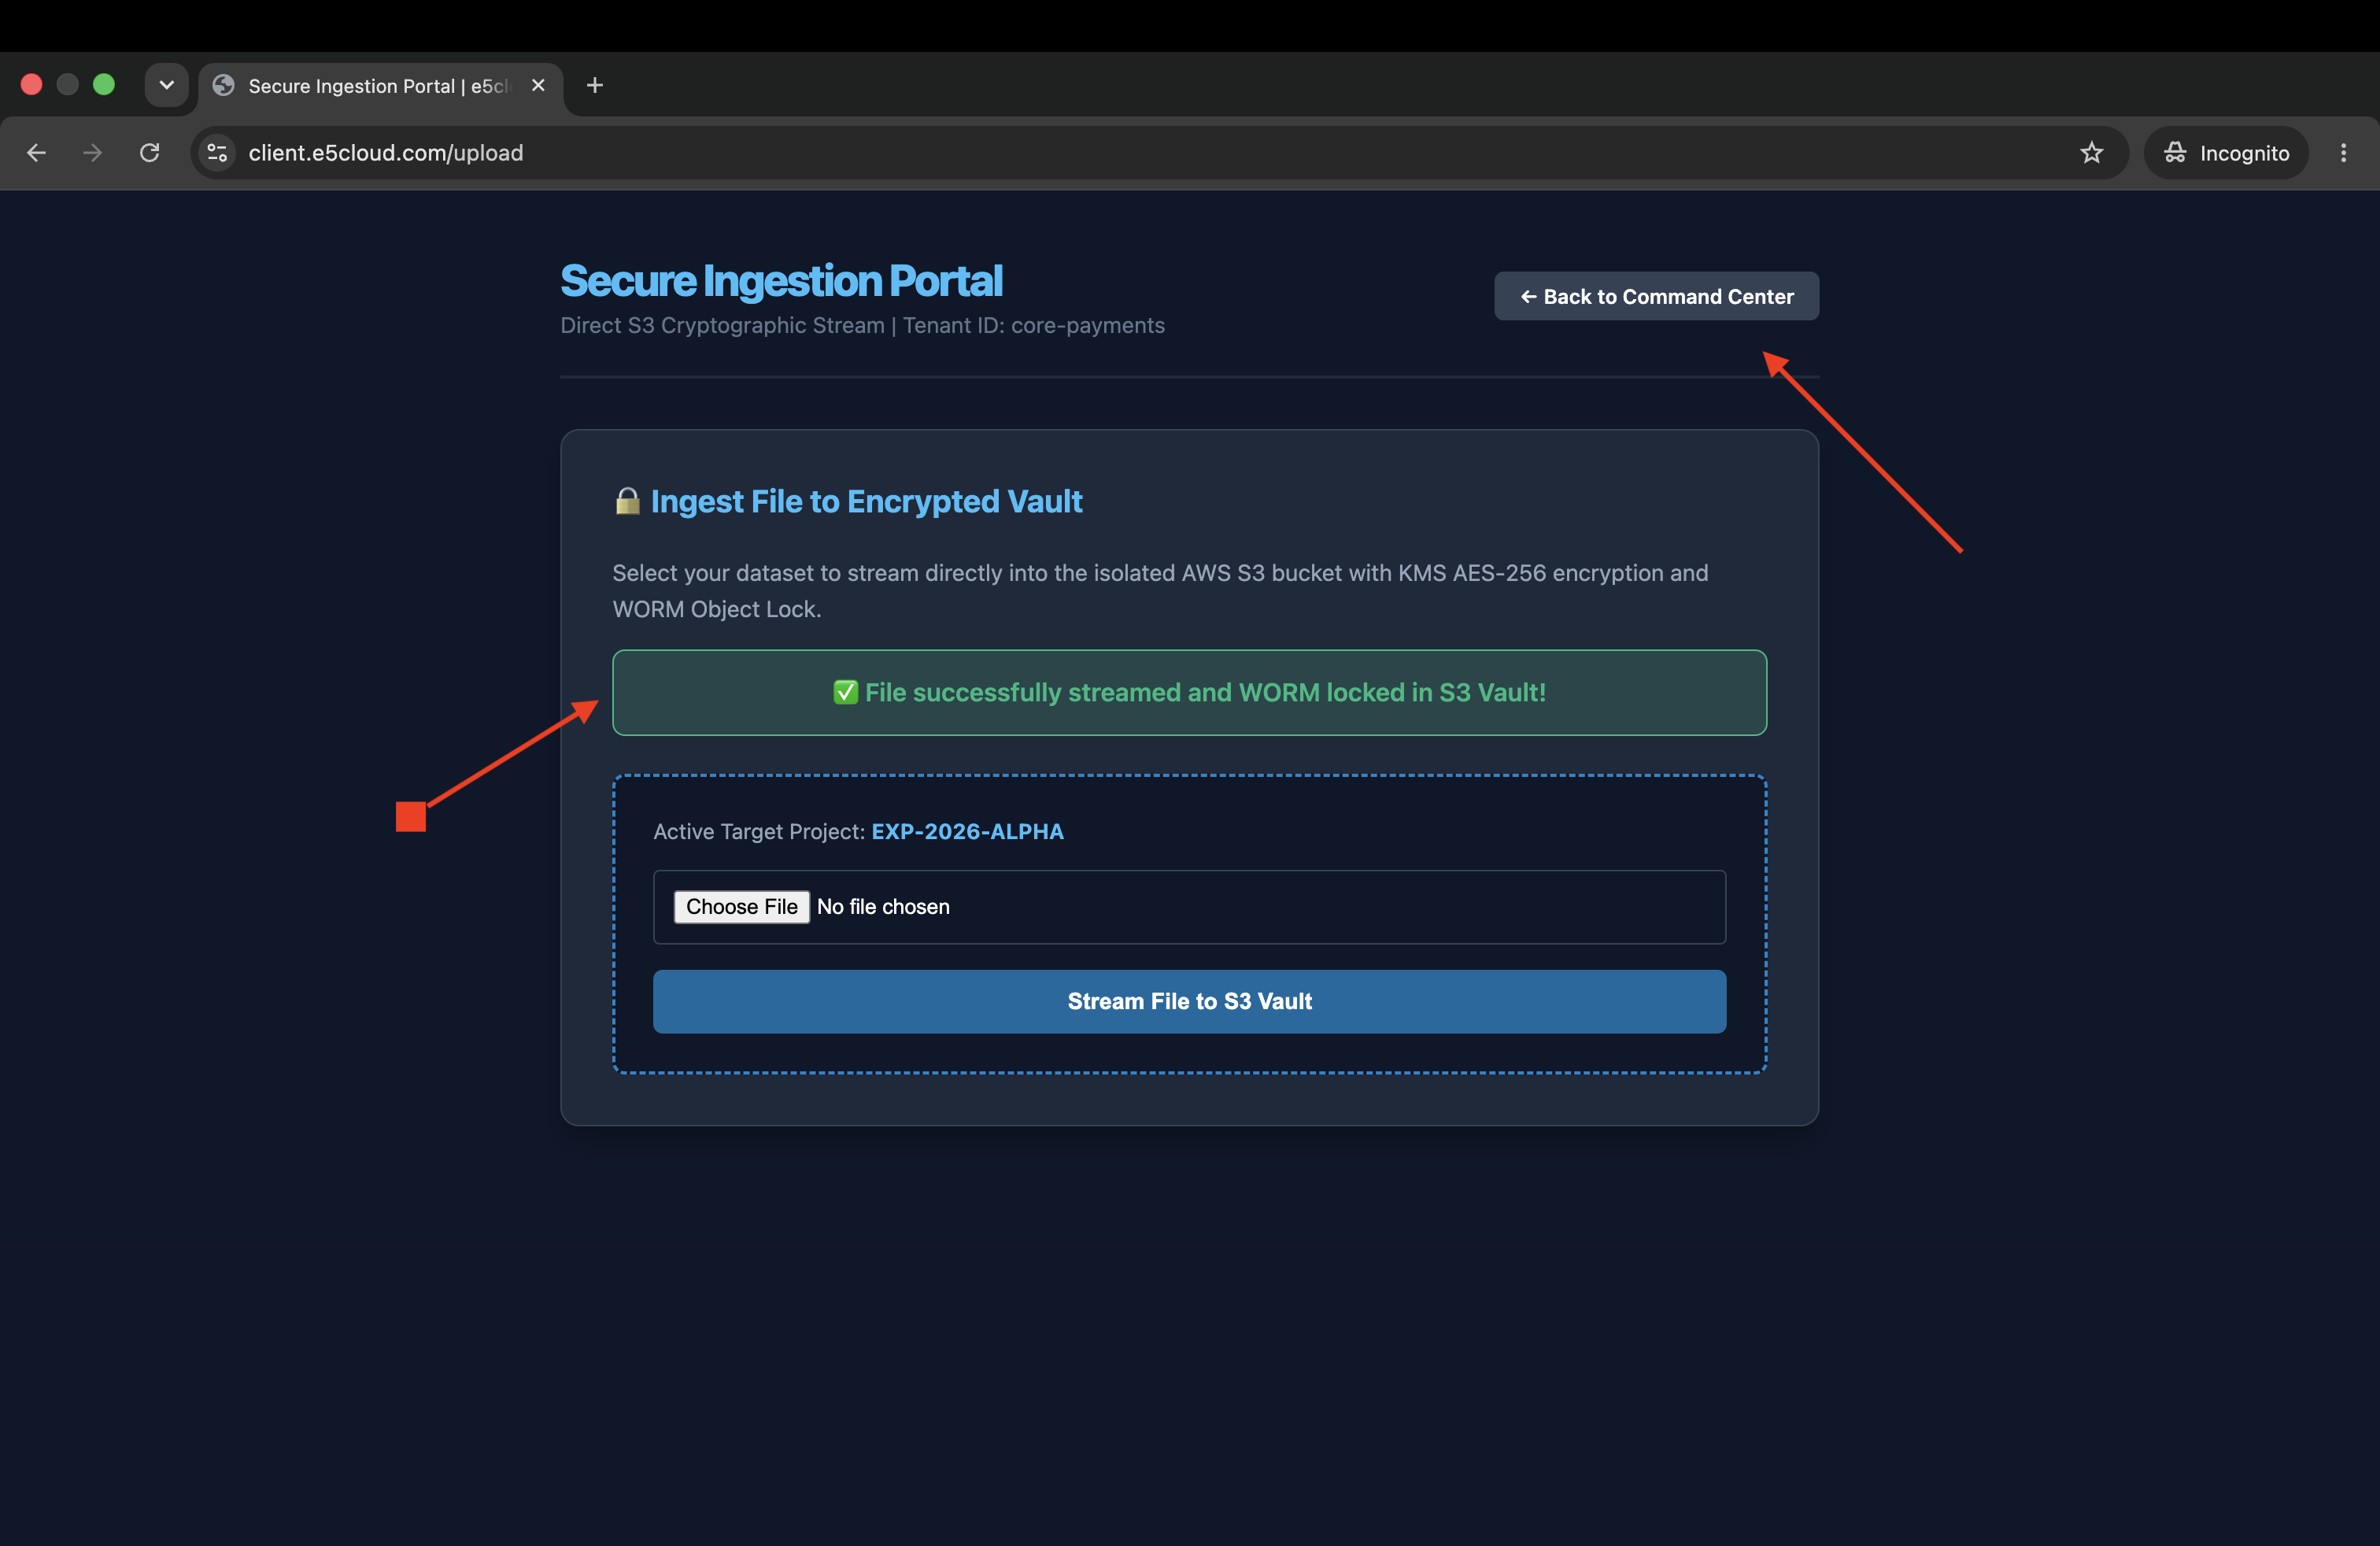
5. Successful Stream & WORM Lock Confirmation:
Real-time telemetry indicating successful file stream completion and immutable vault sealing.
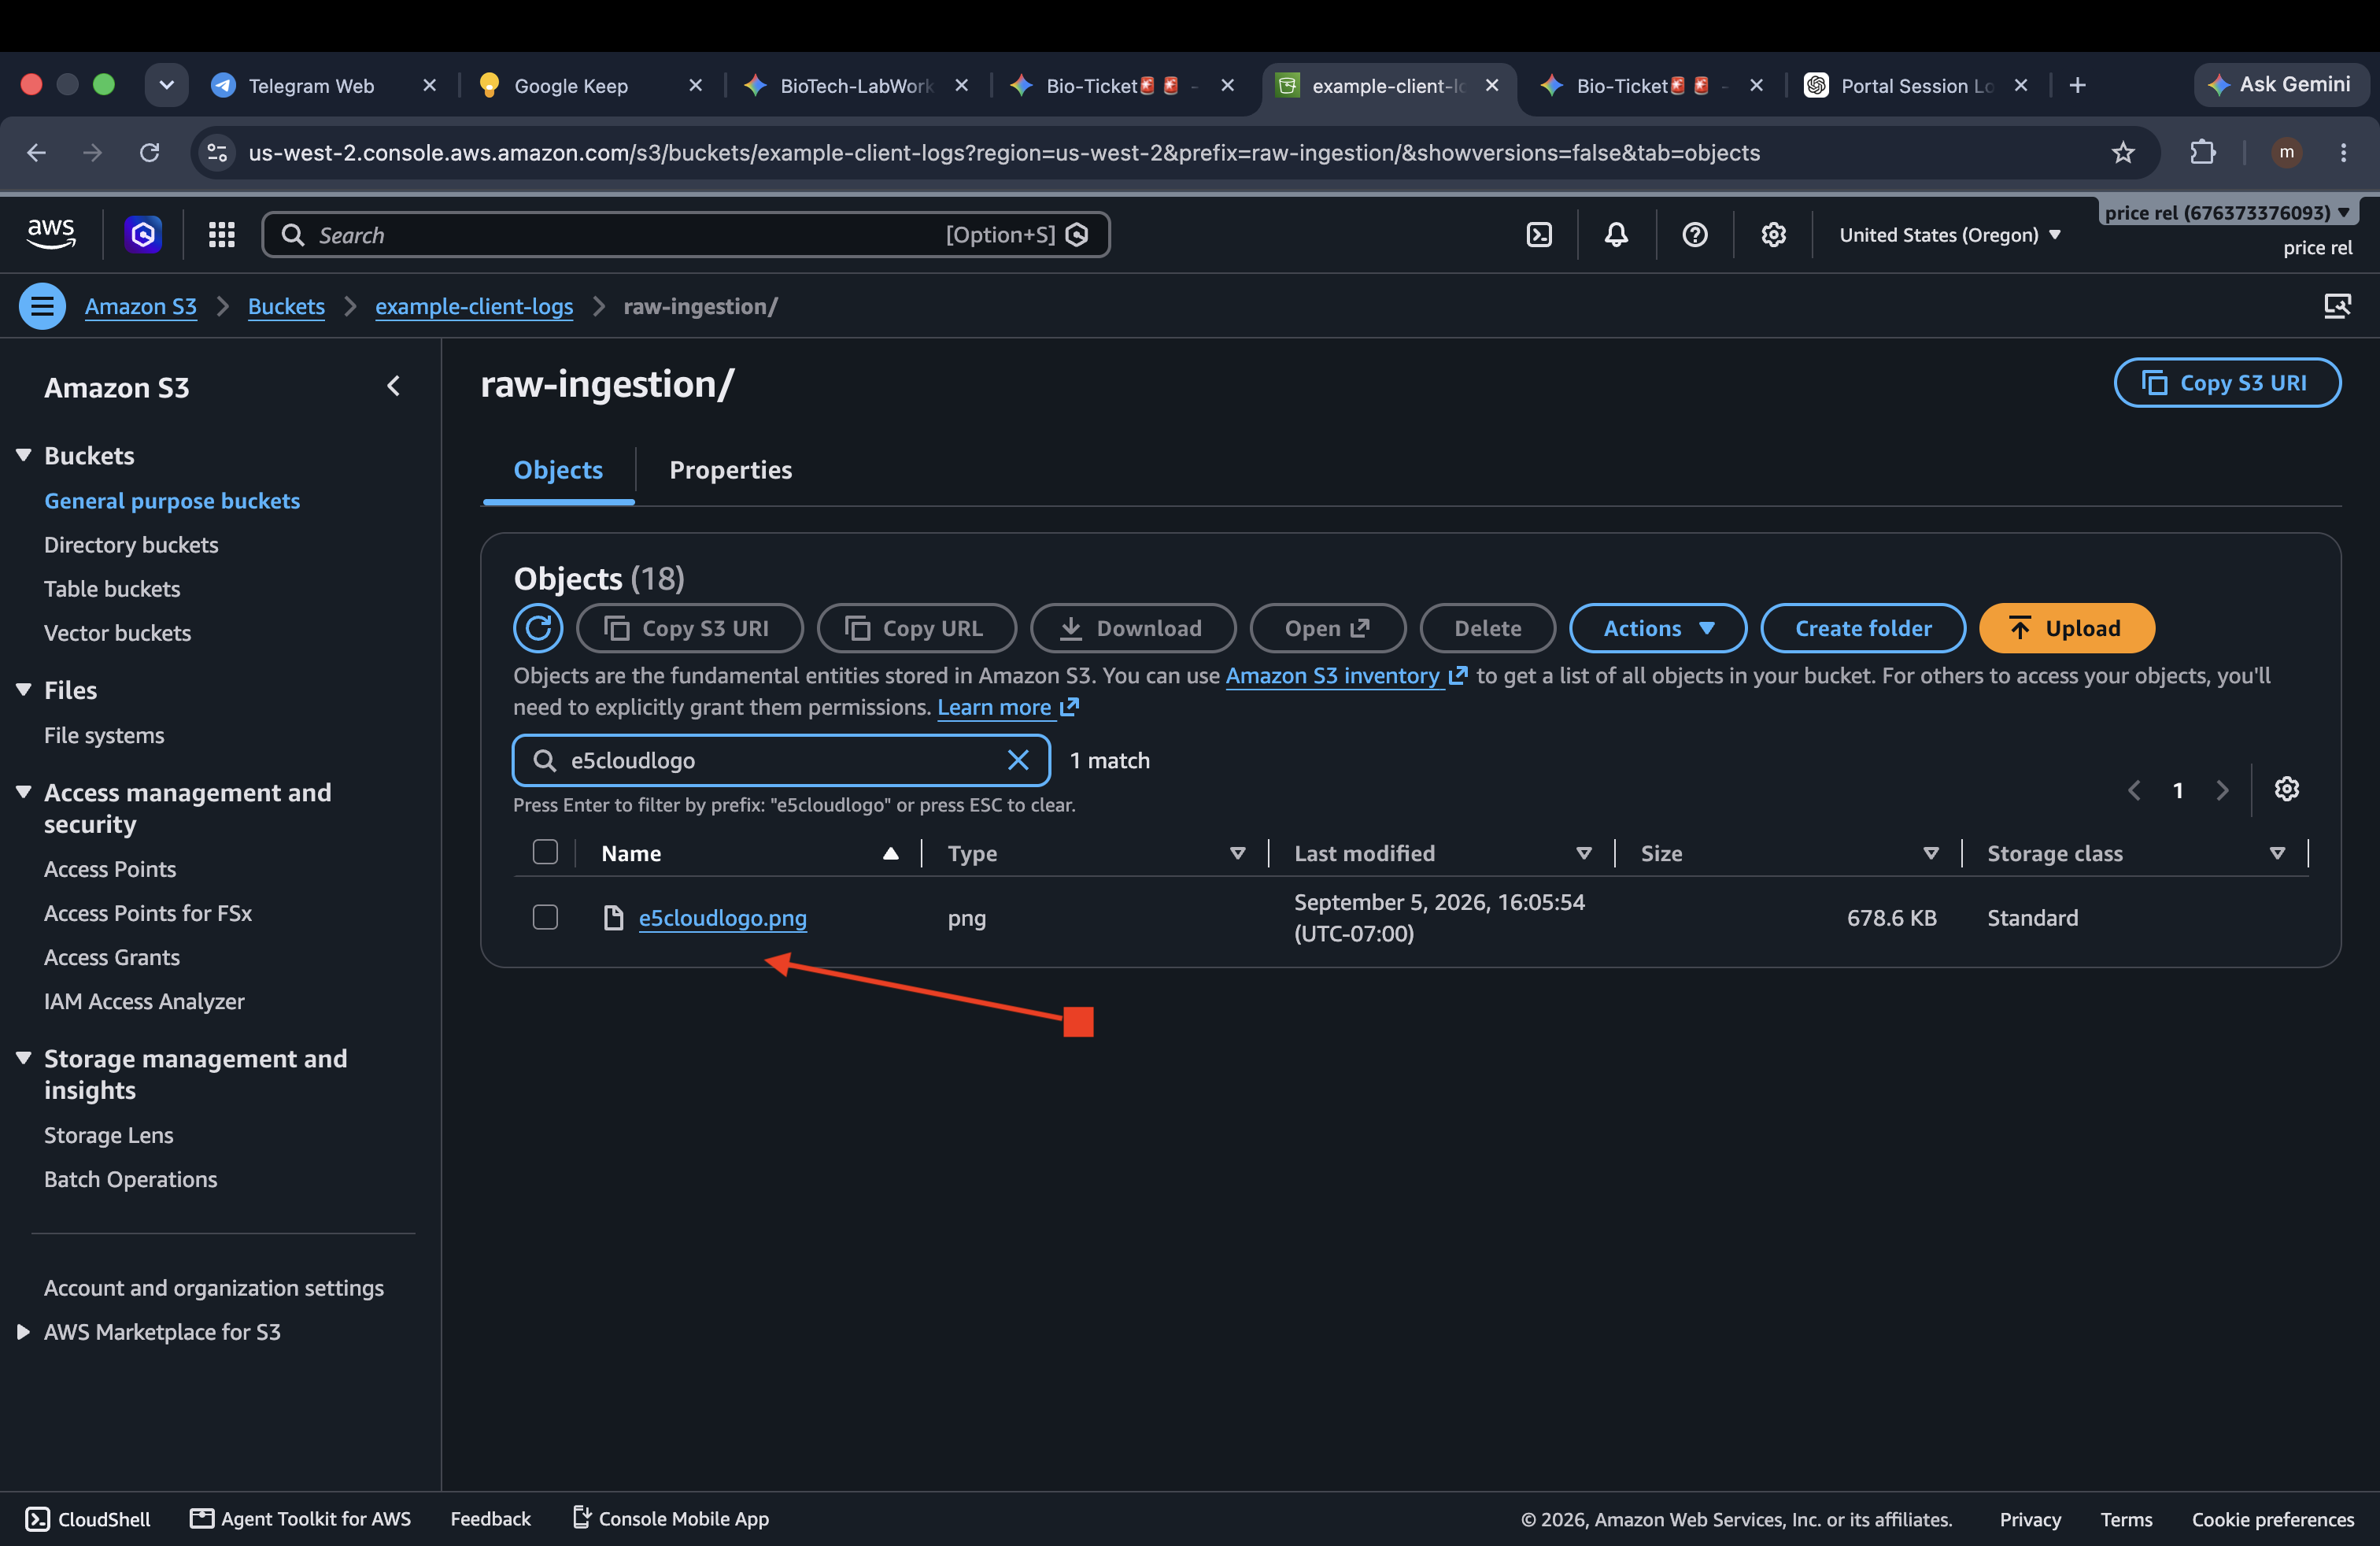
6. AWS S3 Storage Vault Object Verification:
Amazon S3 console confirmation displaying the ingested object (`e5cloudlogo.png`) secured within the raw-ingestion bucket prefix.
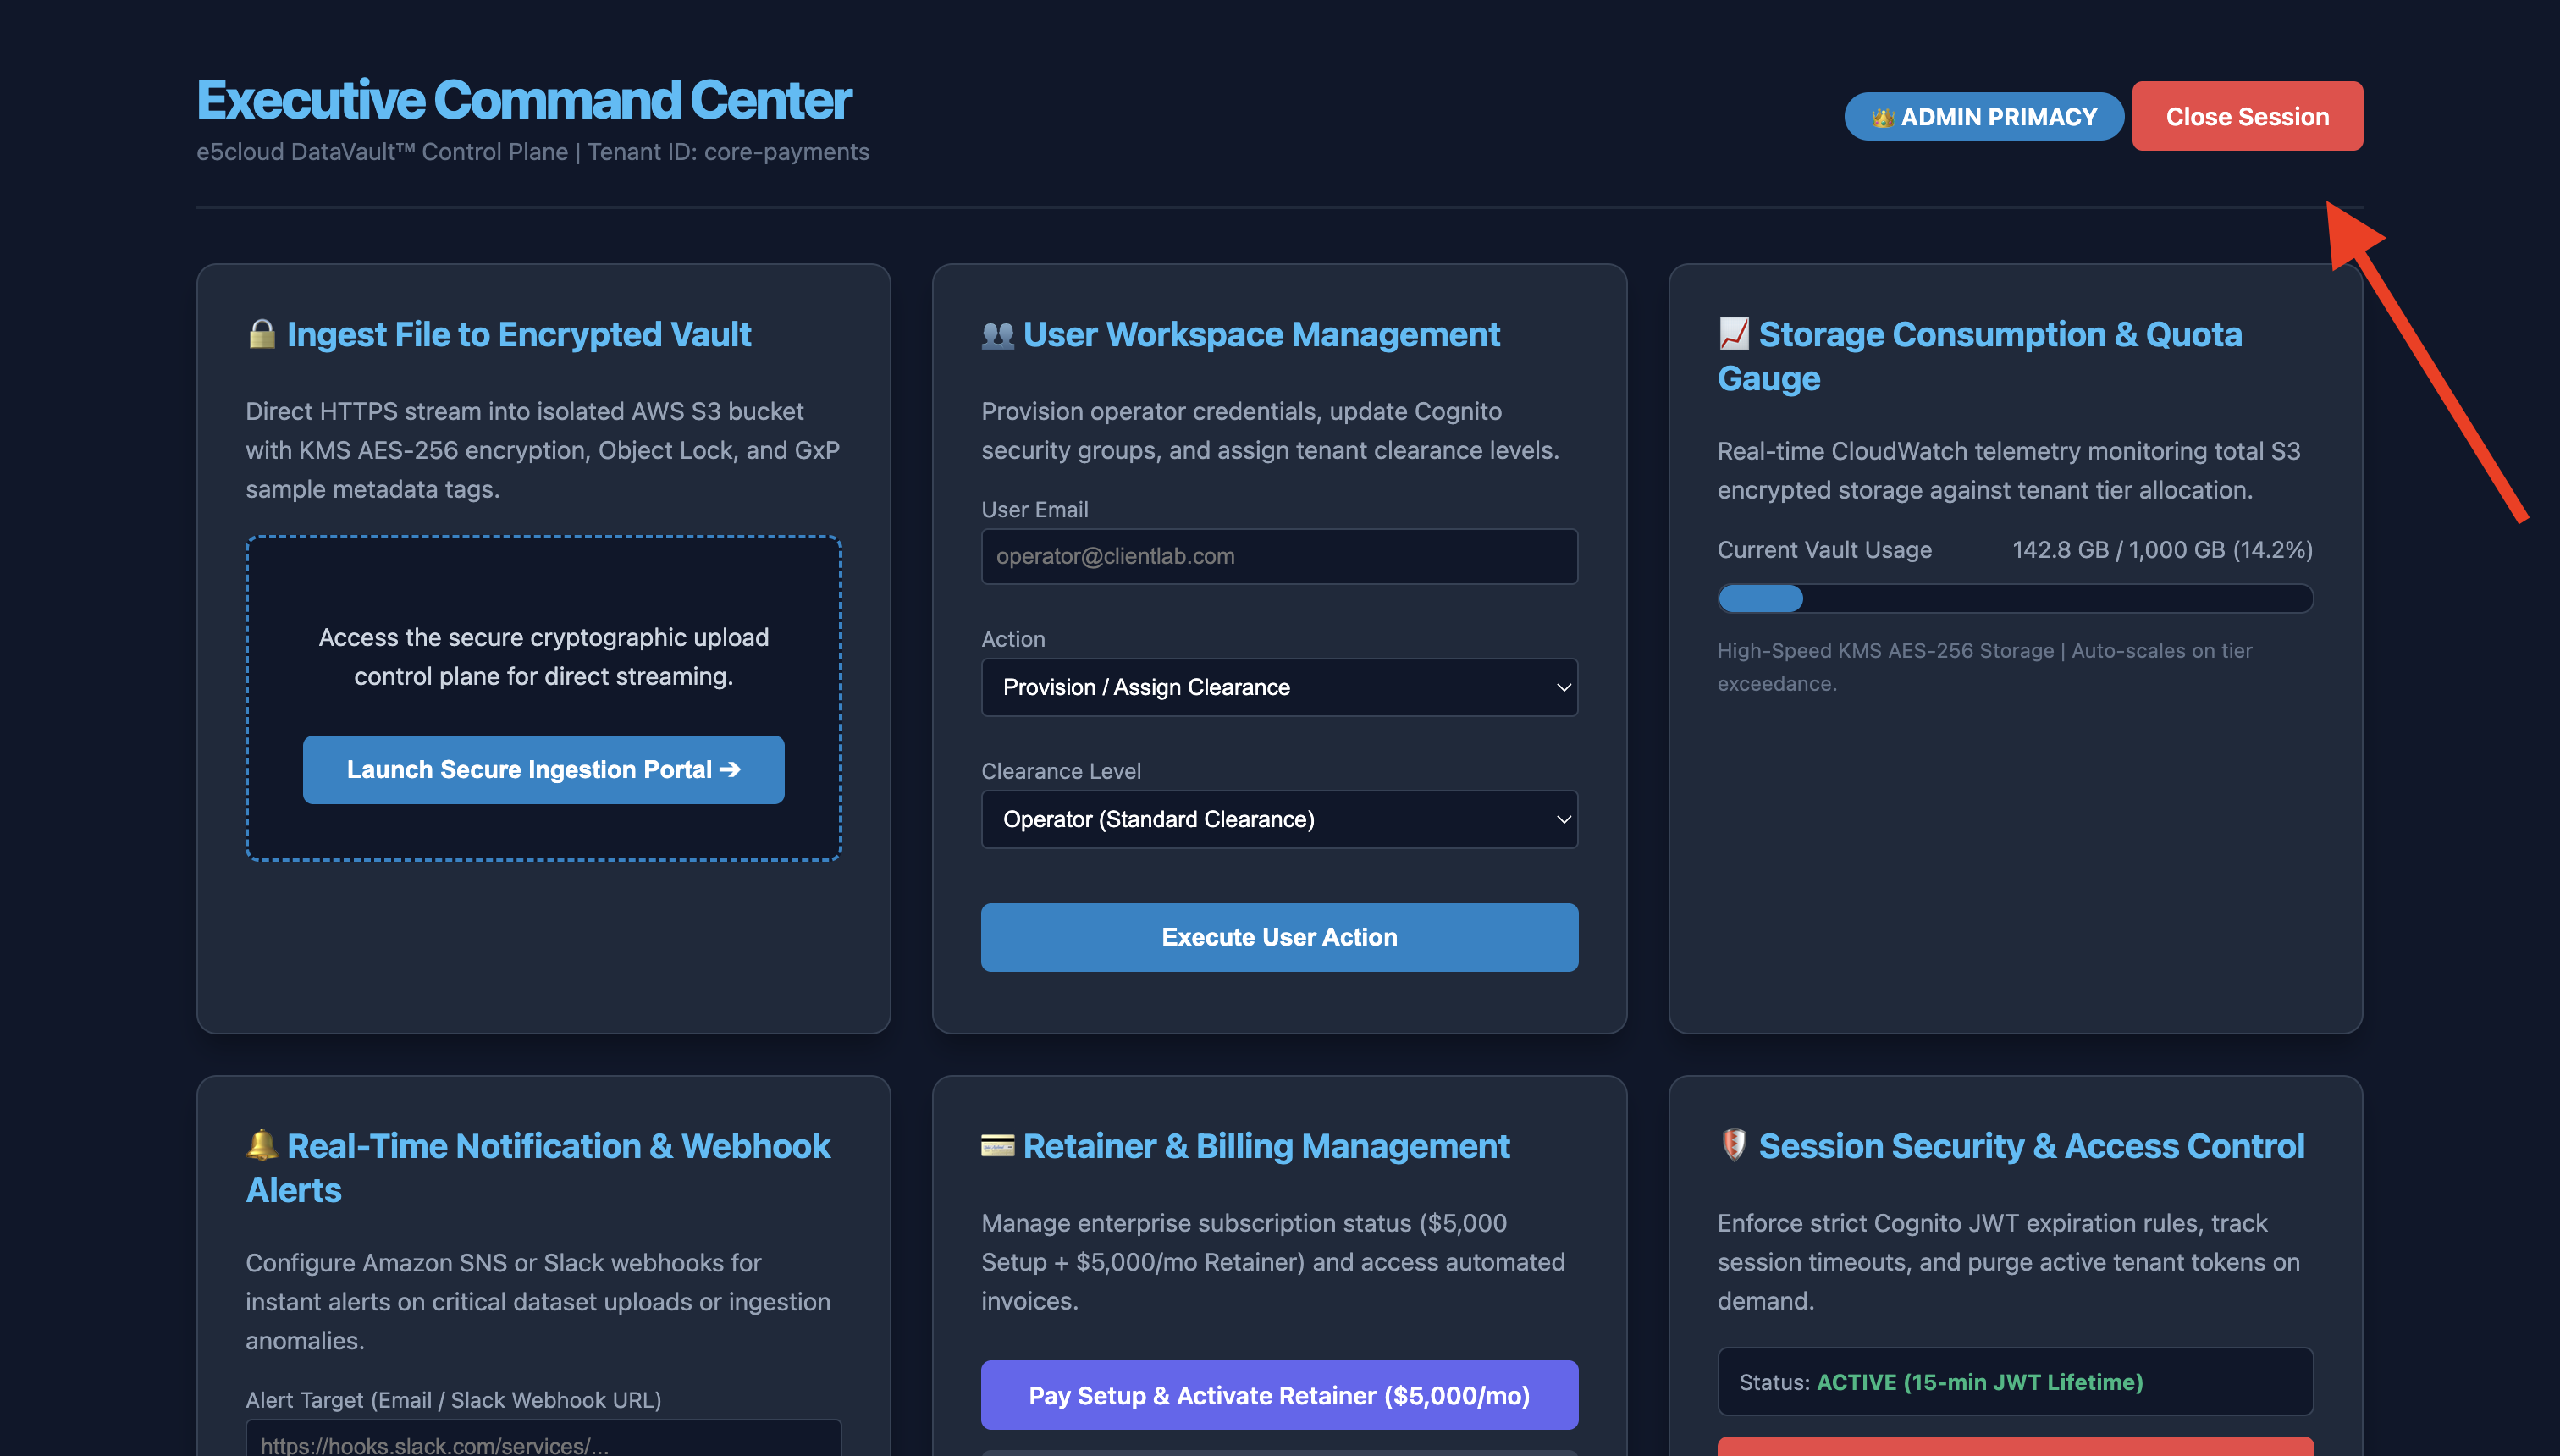
7. Executive Session Termination Control:
Administrative command center view highlighting the "Close Session" action trigger for instant token revocation.
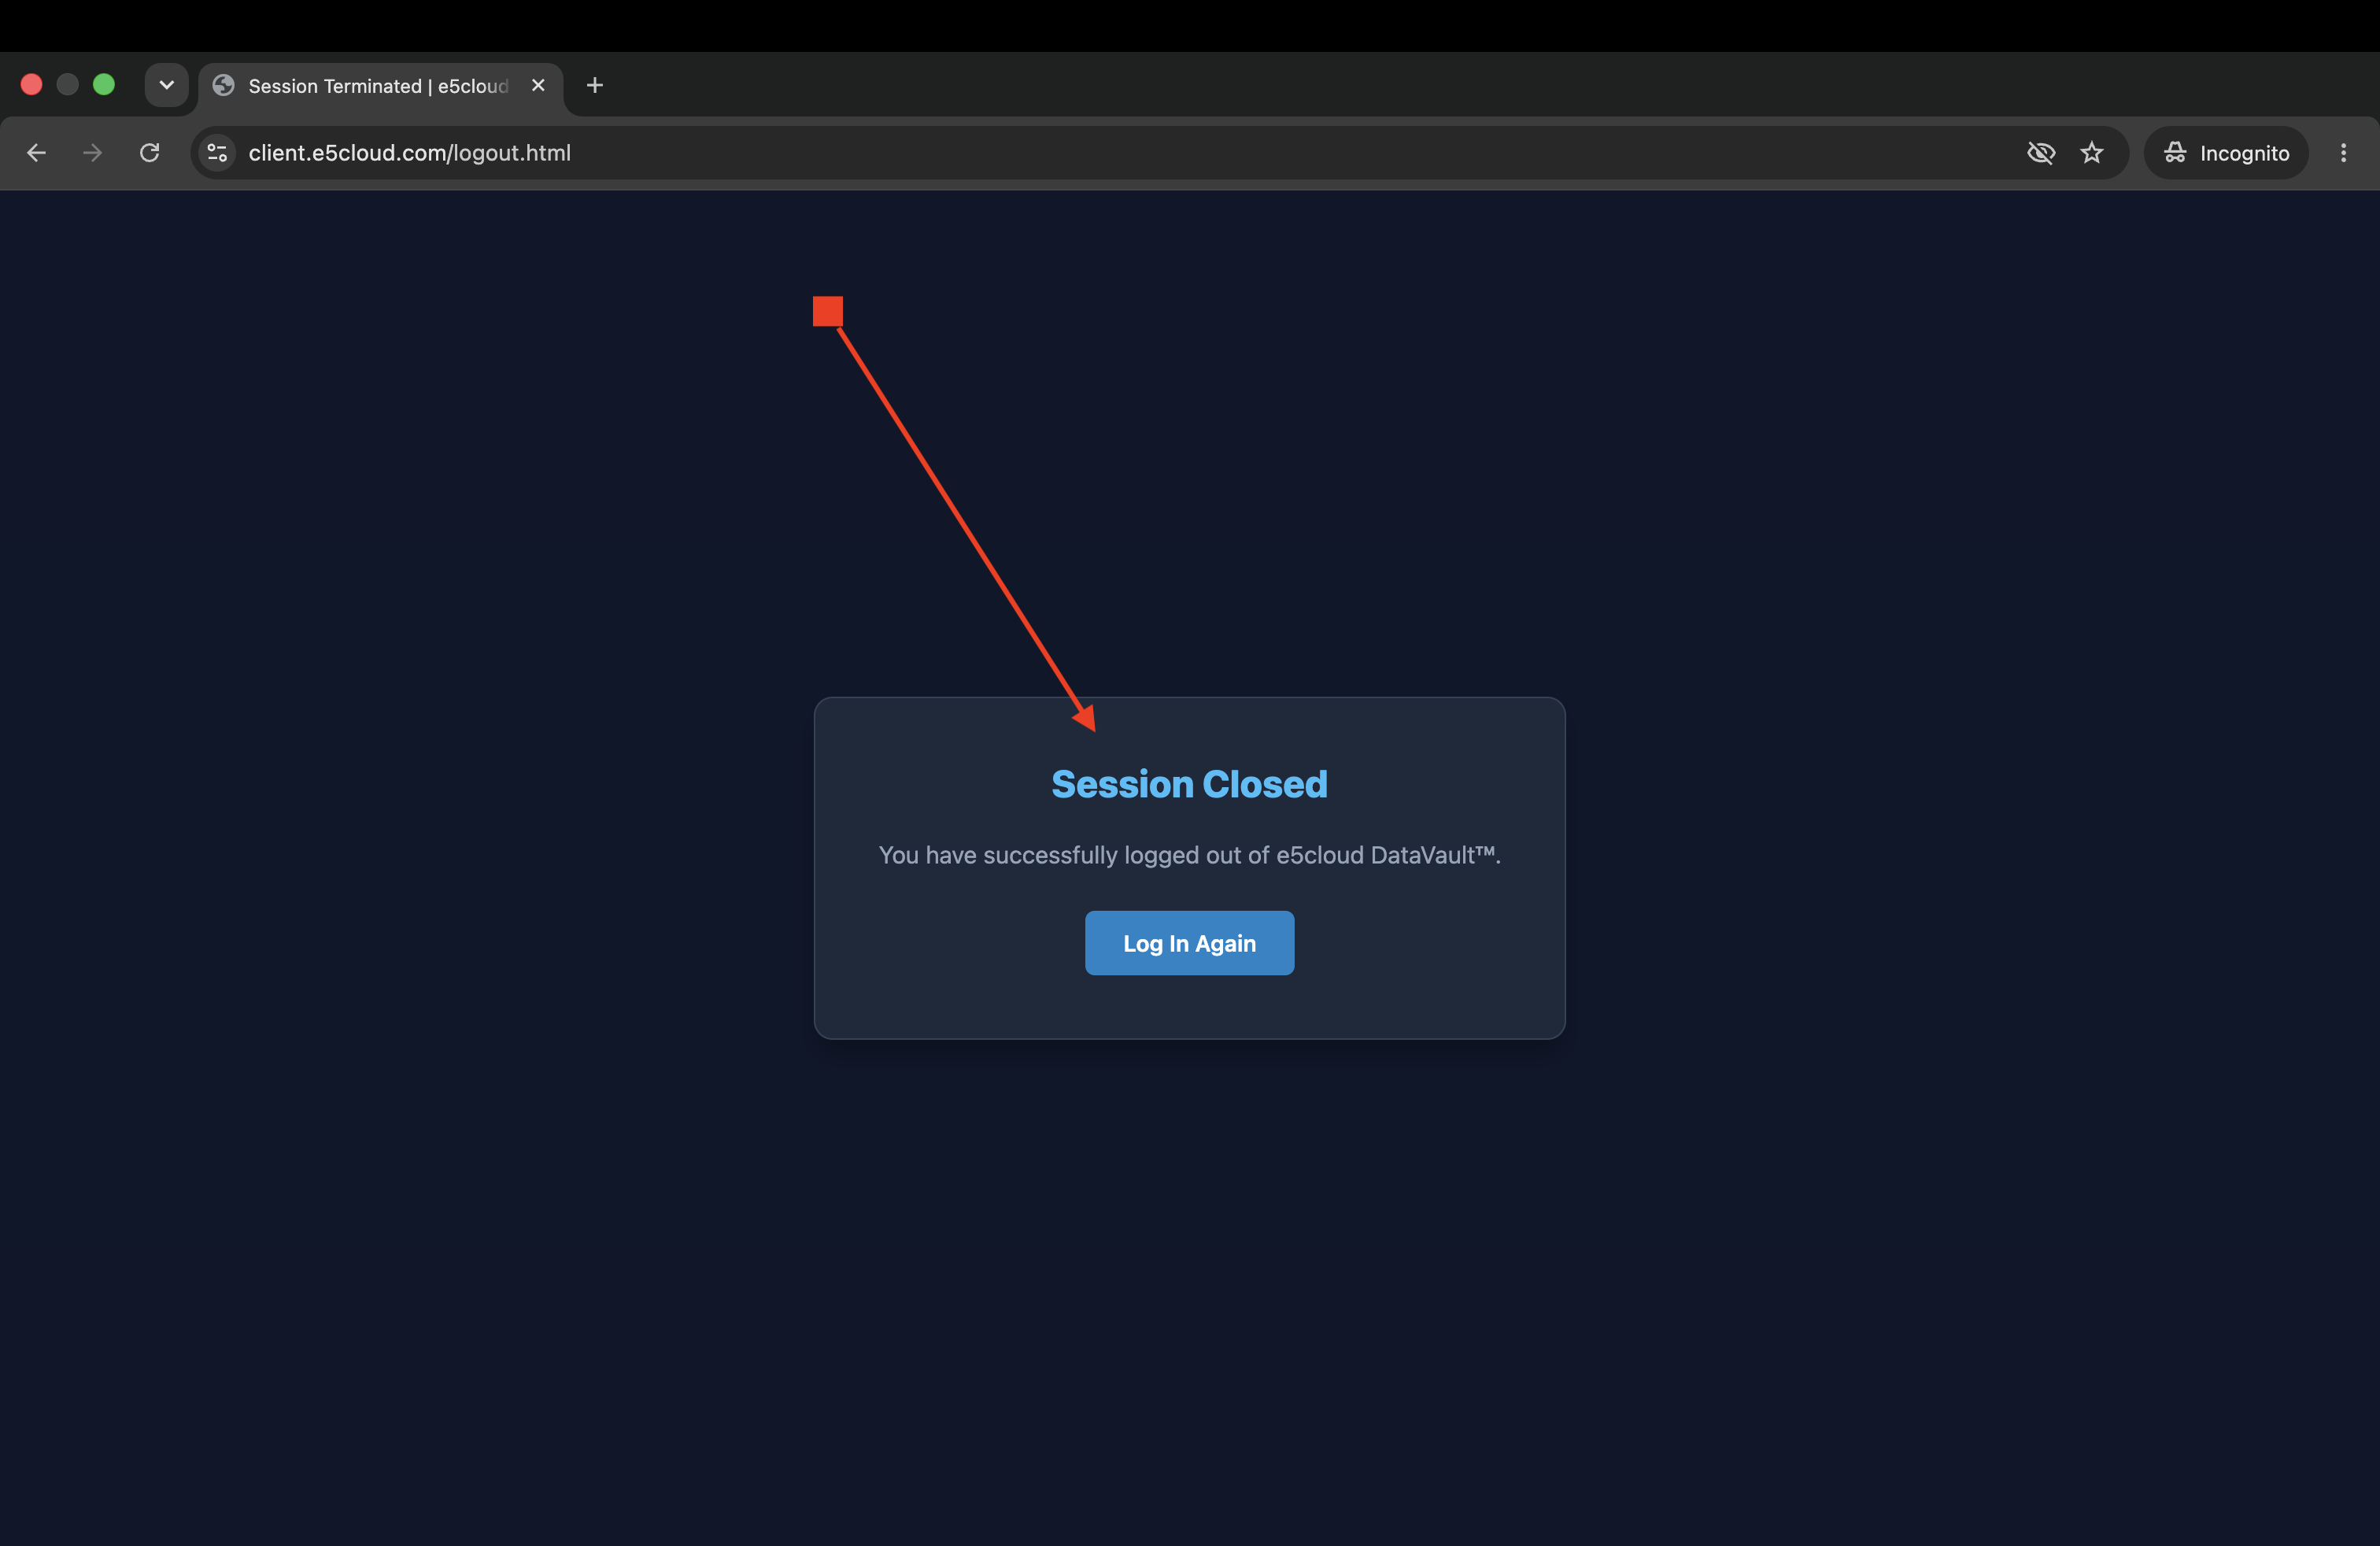
8. Secure Logout & Session Closure:
Confirmation interface at logout.html validating complete token purging and secure session termination.
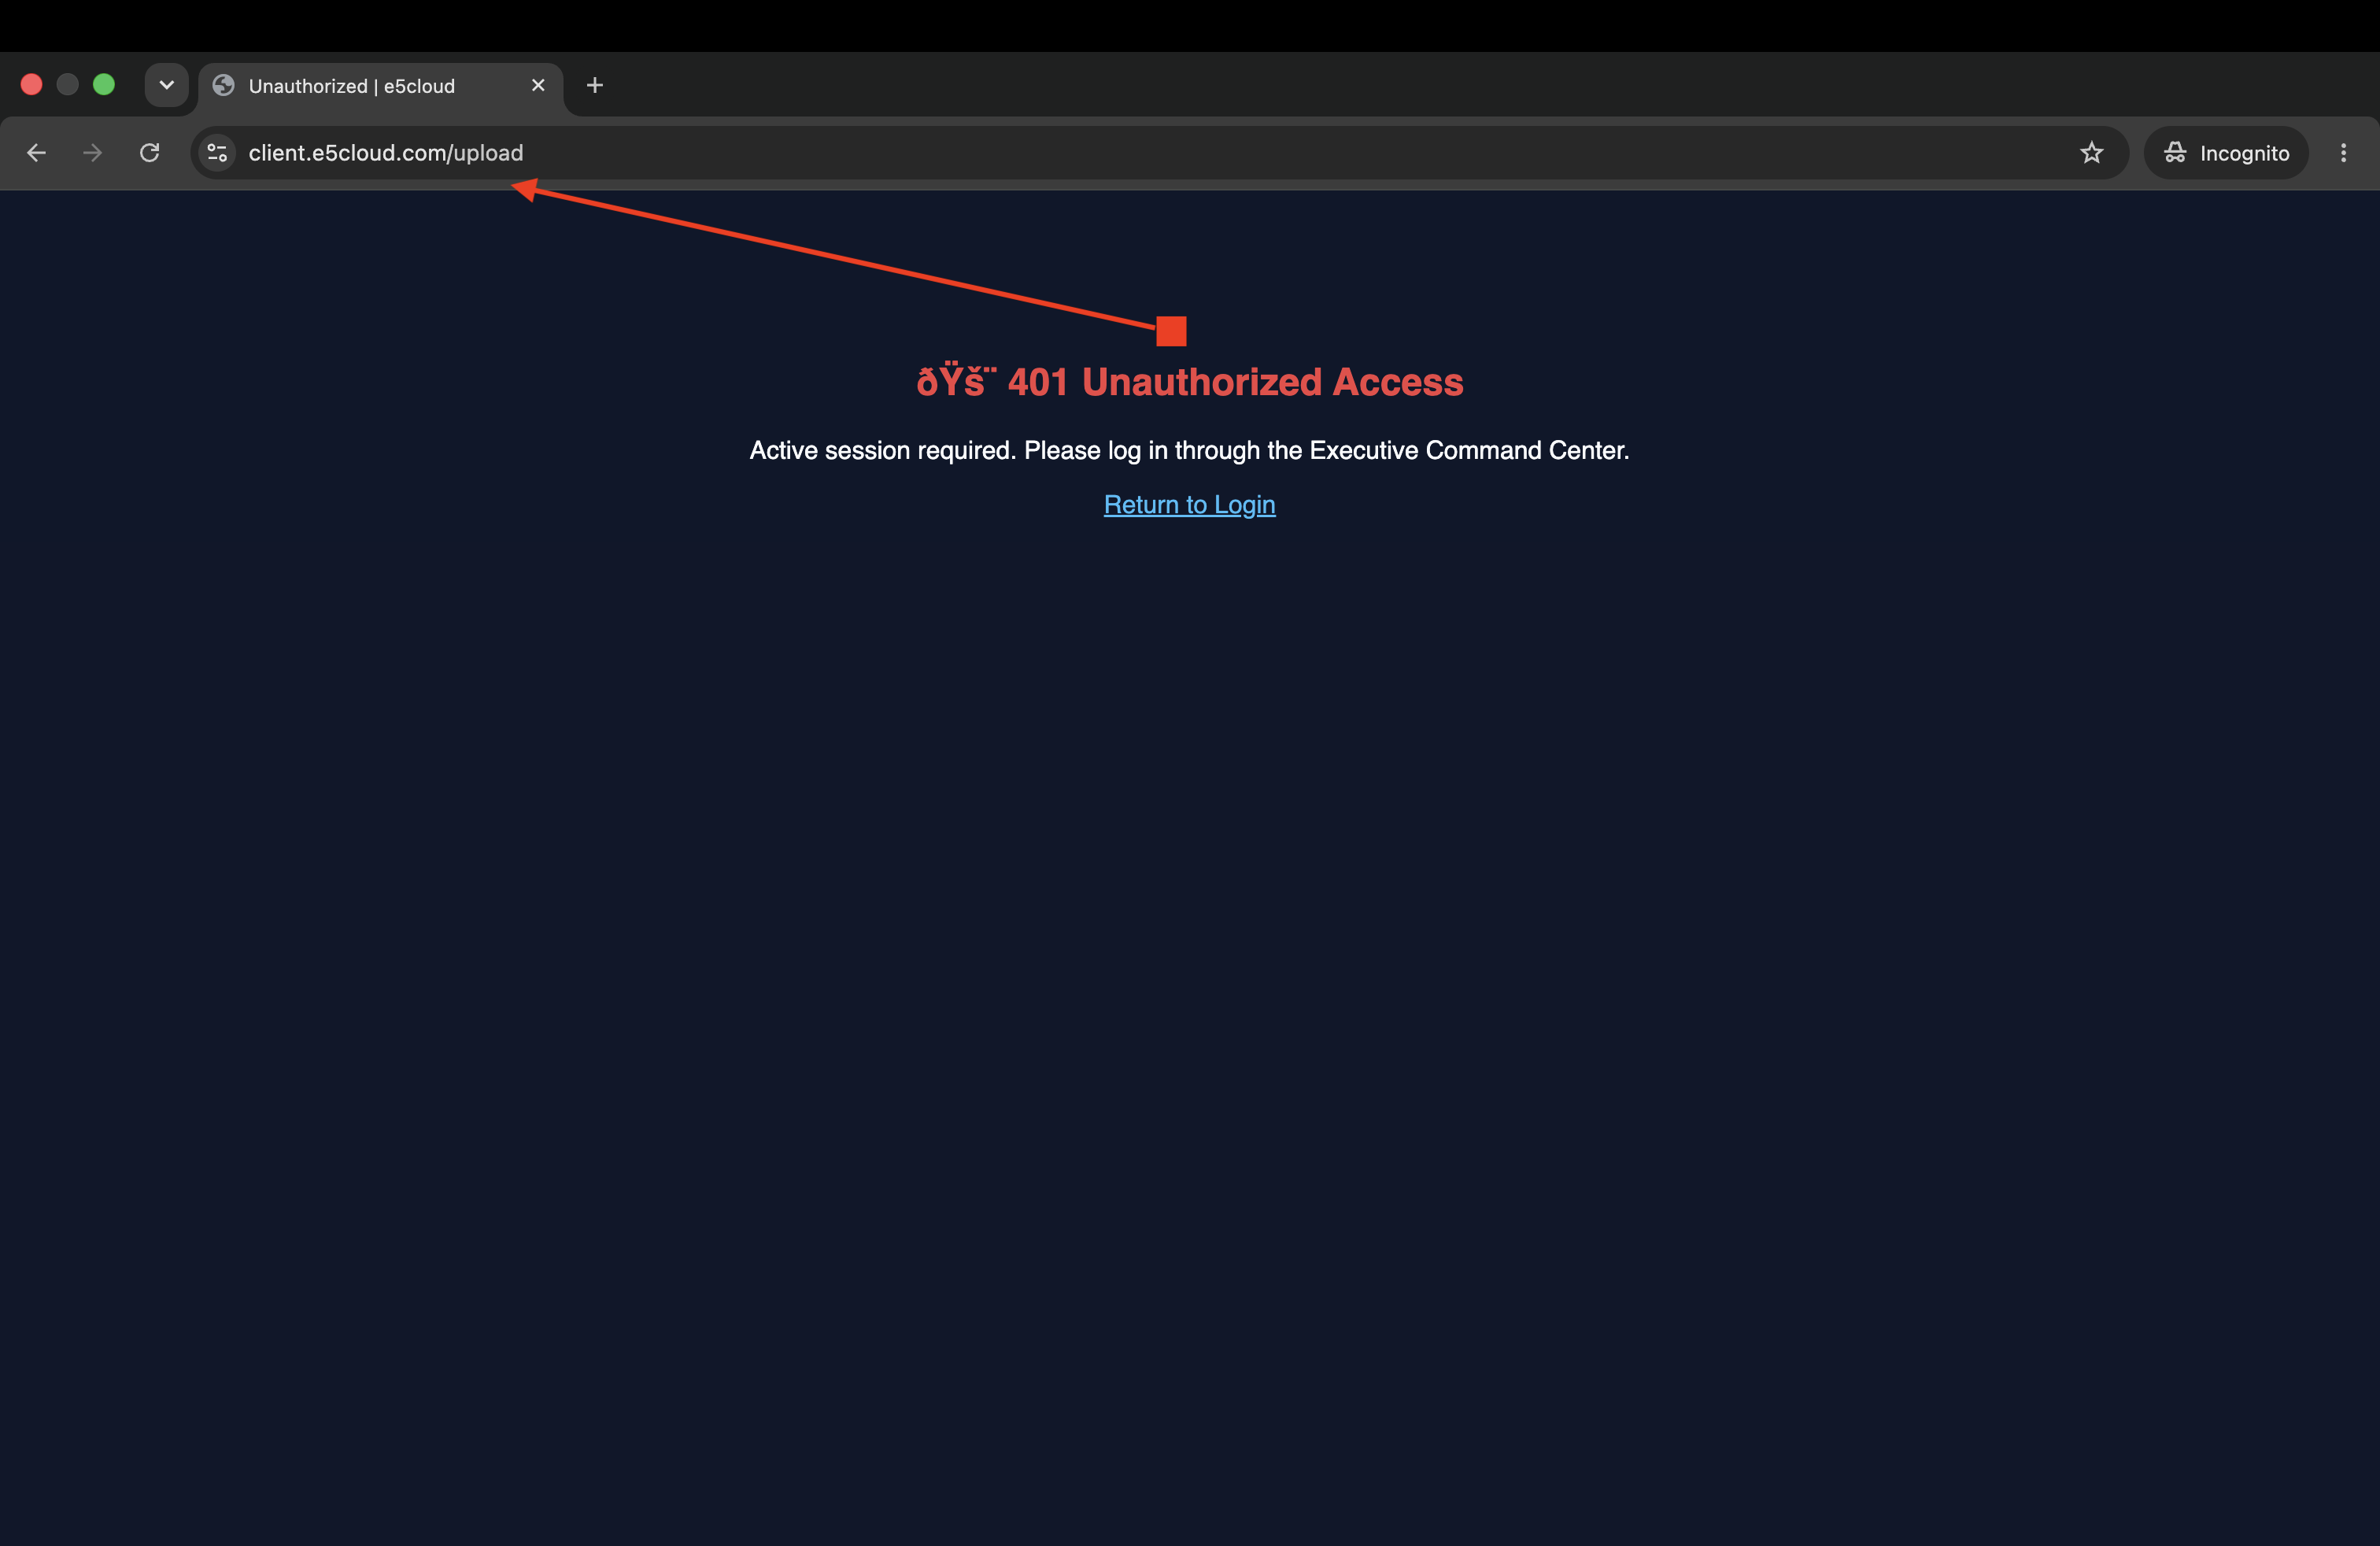
9. Unauthenticated Upload Access Block:
Enforced 401 Unauthorized response when attempting direct navigation to /upload without an active session token.
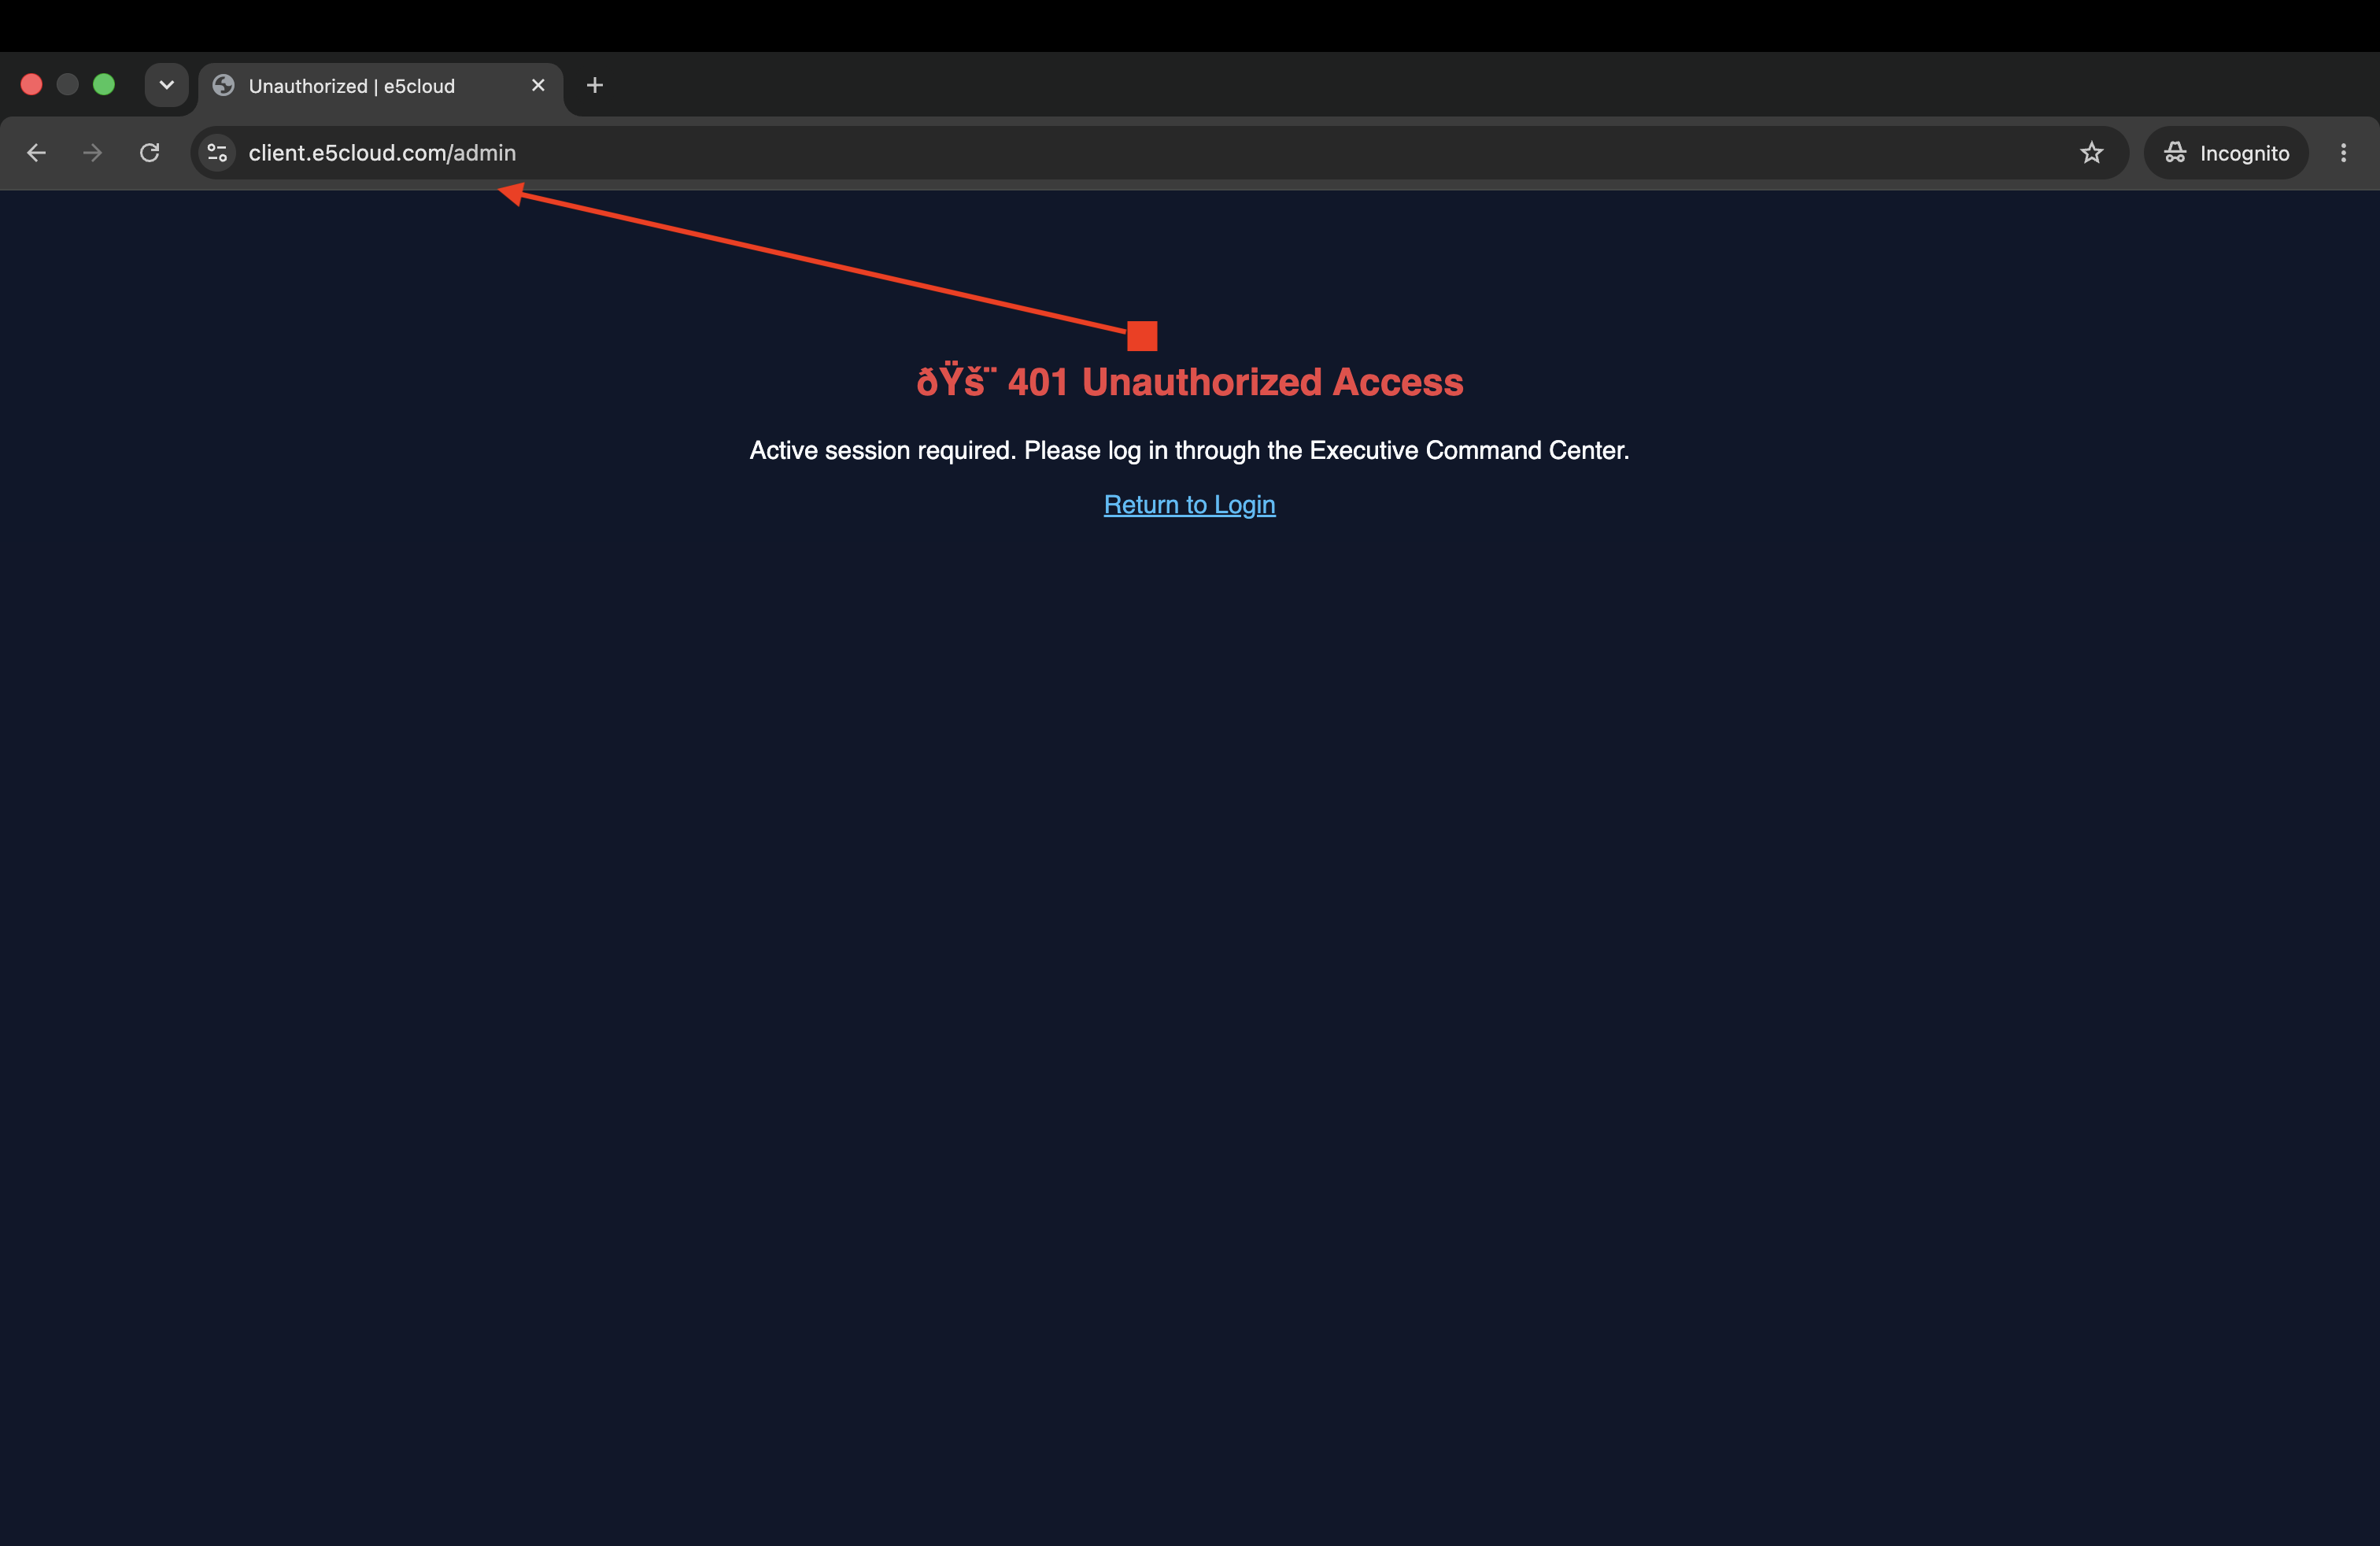
10. Unauthenticated Admin Console Access Block:
Enforced 401 Unauthorized response when attempting direct navigation to /admin without valid authentication credentials.
11. API Gateway Missing Token Enforcement:
Direct API Gateway invocation response returning {"message":"Missing Authentication Token"}, confirming strict API perimeter defenses.