Object Integrity & Ingestion Verification:
Validates individual object health and core asset storage states within the secure bucket framework via aws s3api head-object --bucket example-client-logs --key asset.png.
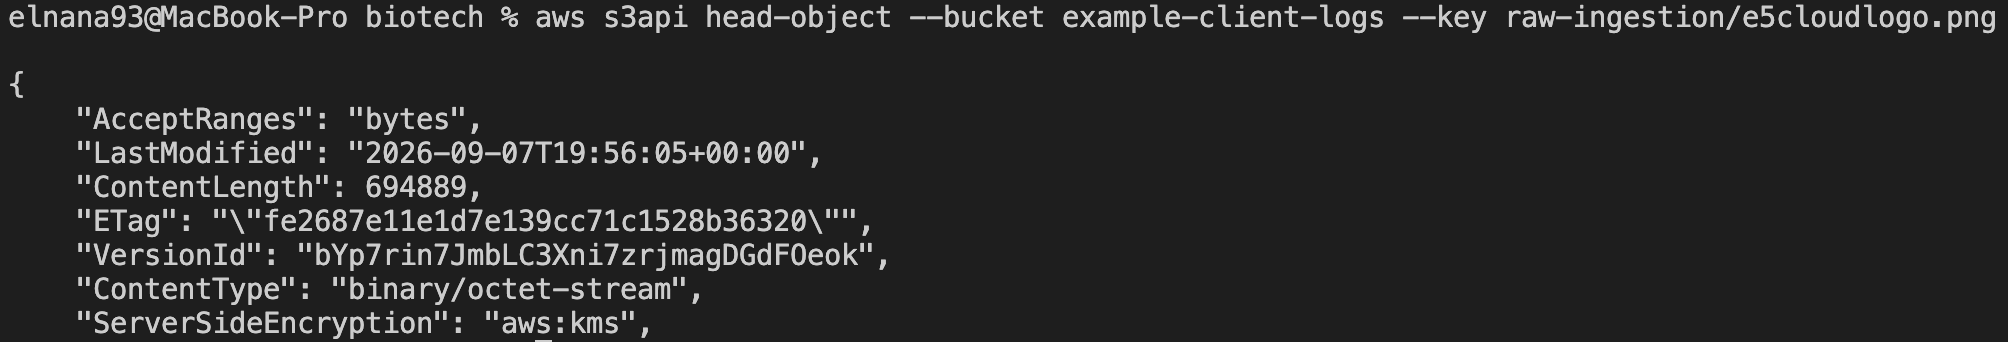
This automated verification process ensures all ingested data meets strict security compliance and cryptographic integrity standards before transitioning to primary storage layers.
Data-at-Rest Encryption Validation (KMS):
Confirms default server-side encryption rules and cryptographic enforcement on target log buckets via aws s3api get-bucket-encryption --bucket example-client-logs.
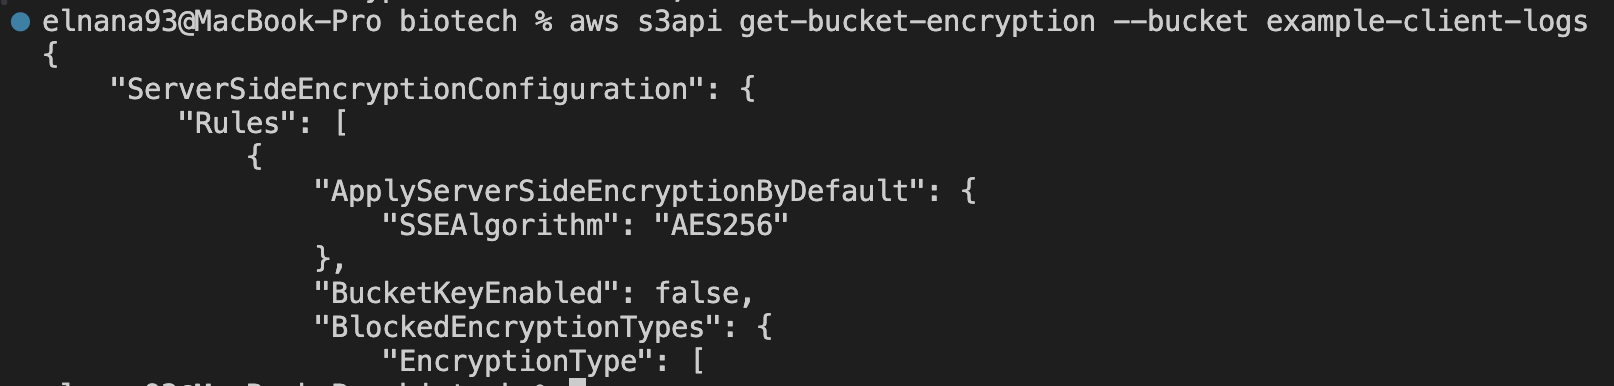
Verifies active SSE-KMS / AES-256 encryption policies across all enterprise log repositories to ensure strict regulatory storage compliance.
Regulatory Immutability & WORM Compliance:
Validates Write-Once-Read-Many (WORM) object lock configurations on target log buckets via aws s3api get-object-lock-configuration --bucket example-client-logs.
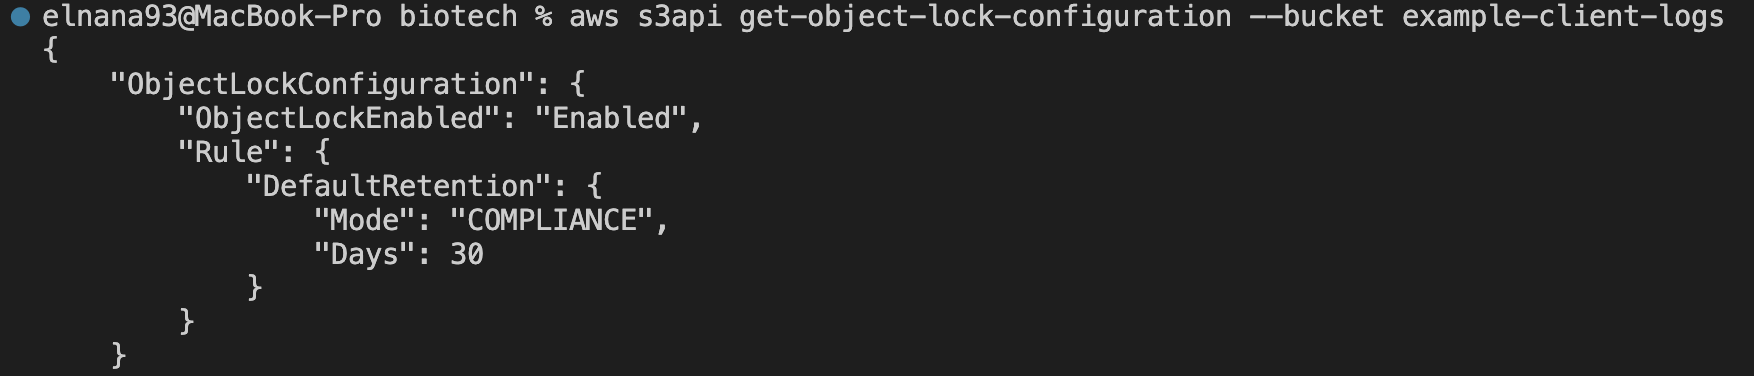
Enforces strict COMPLIANCE mode with a 30-day default retention period to prevent accidental deletion, overwrite, or tampering of enterprise regulatory records.
Network Isolation & Public Exposure Prevention:
Validates strict S3 Block Public Access configurations on target log buckets via aws s3api get-public-access-block --bucket example-client-logs.
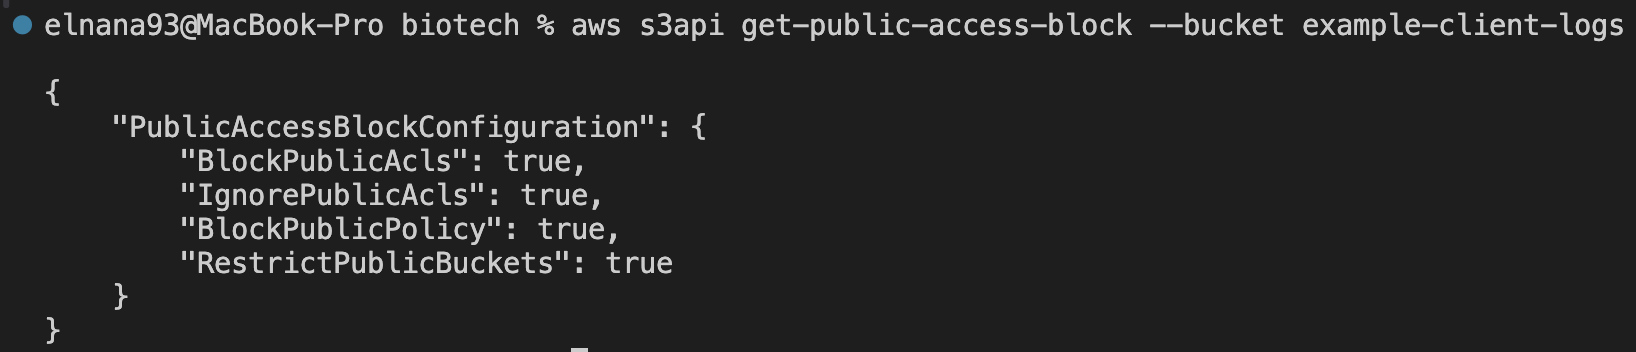
Confirms all four public access blocks are actively set to true (BlockPublicAcls, IgnorePublicAcls, BlockPublicPolicy, RestrictPublicBuckets), enforcing complete zero-trust network isolation.
Access Auditing & Server Traceability:
Validates target bucket server access logging configurations via aws s3api get-bucket-logging --bucket example-client-logs.
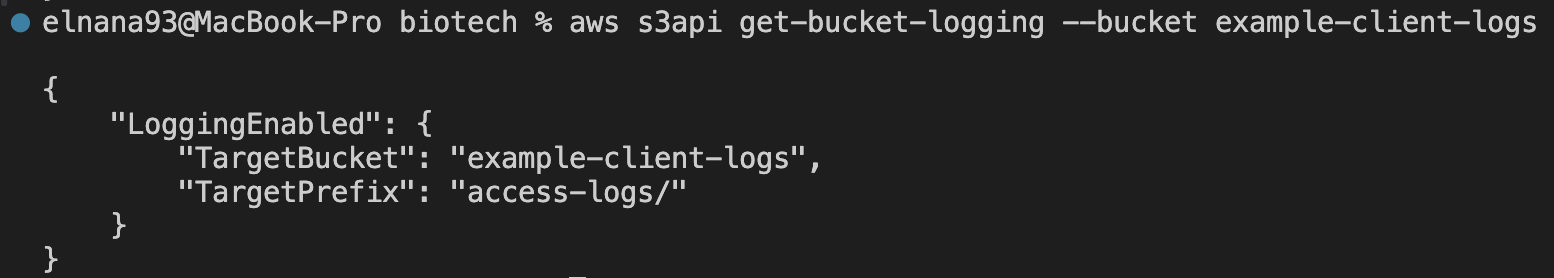
Verifies active server access logging enabled to capture all incoming bucket requests into the dedicated access-logs/ prefix for end-to-end security auditability and regulatory compliance.
Data-in-Transit (TLS/HTTPS) Enforcement:
Validates strict bucket policy transport restrictions via aws s3api get-bucket-policy --bucket example-client-logs.
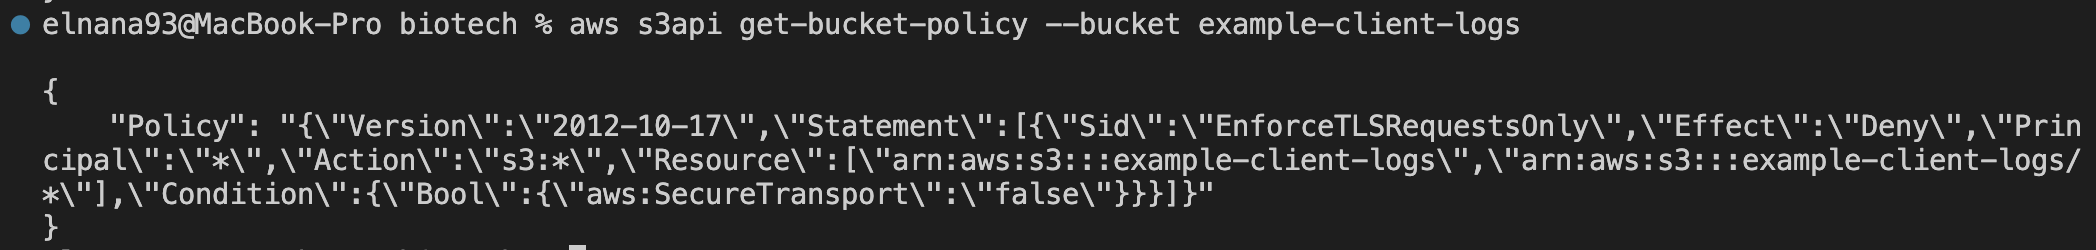
Verifies active bucket policy rules enforcing EnforceTLSRequestsOnly to explicitly deny any non-HTTPS unencrypted connections (aws:SecureTransport: false), securing all asset requests in transit.
Client Secure Upload Endpoint Validation:
Validates edge security behavior for unauthenticated ingestion requests via curl -i -X POST https://client.e5cloud.com/upload.
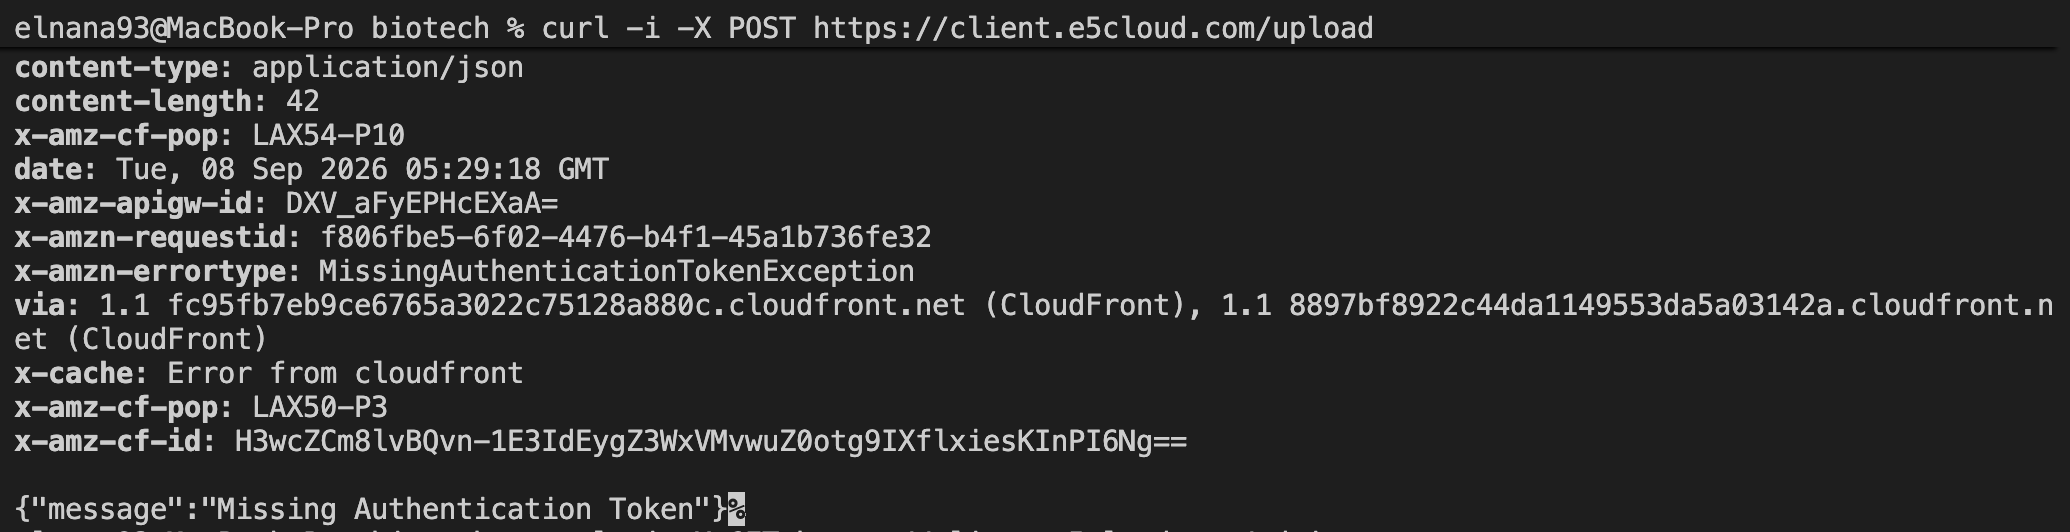
Used during security audits to verify that unauthenticated ingestion requests routed through the custom domain are instantly dropped at the edge with an HTTP/2 403 Forbidden (MissingAuthenticationTokenException), enforcing strict zero-trust API protection.
Administrative Portal Access Control Verification:
Validates perimeter enforcement on restricted management planes via curl -i -X GET https://client.e5cloud.com/admin.
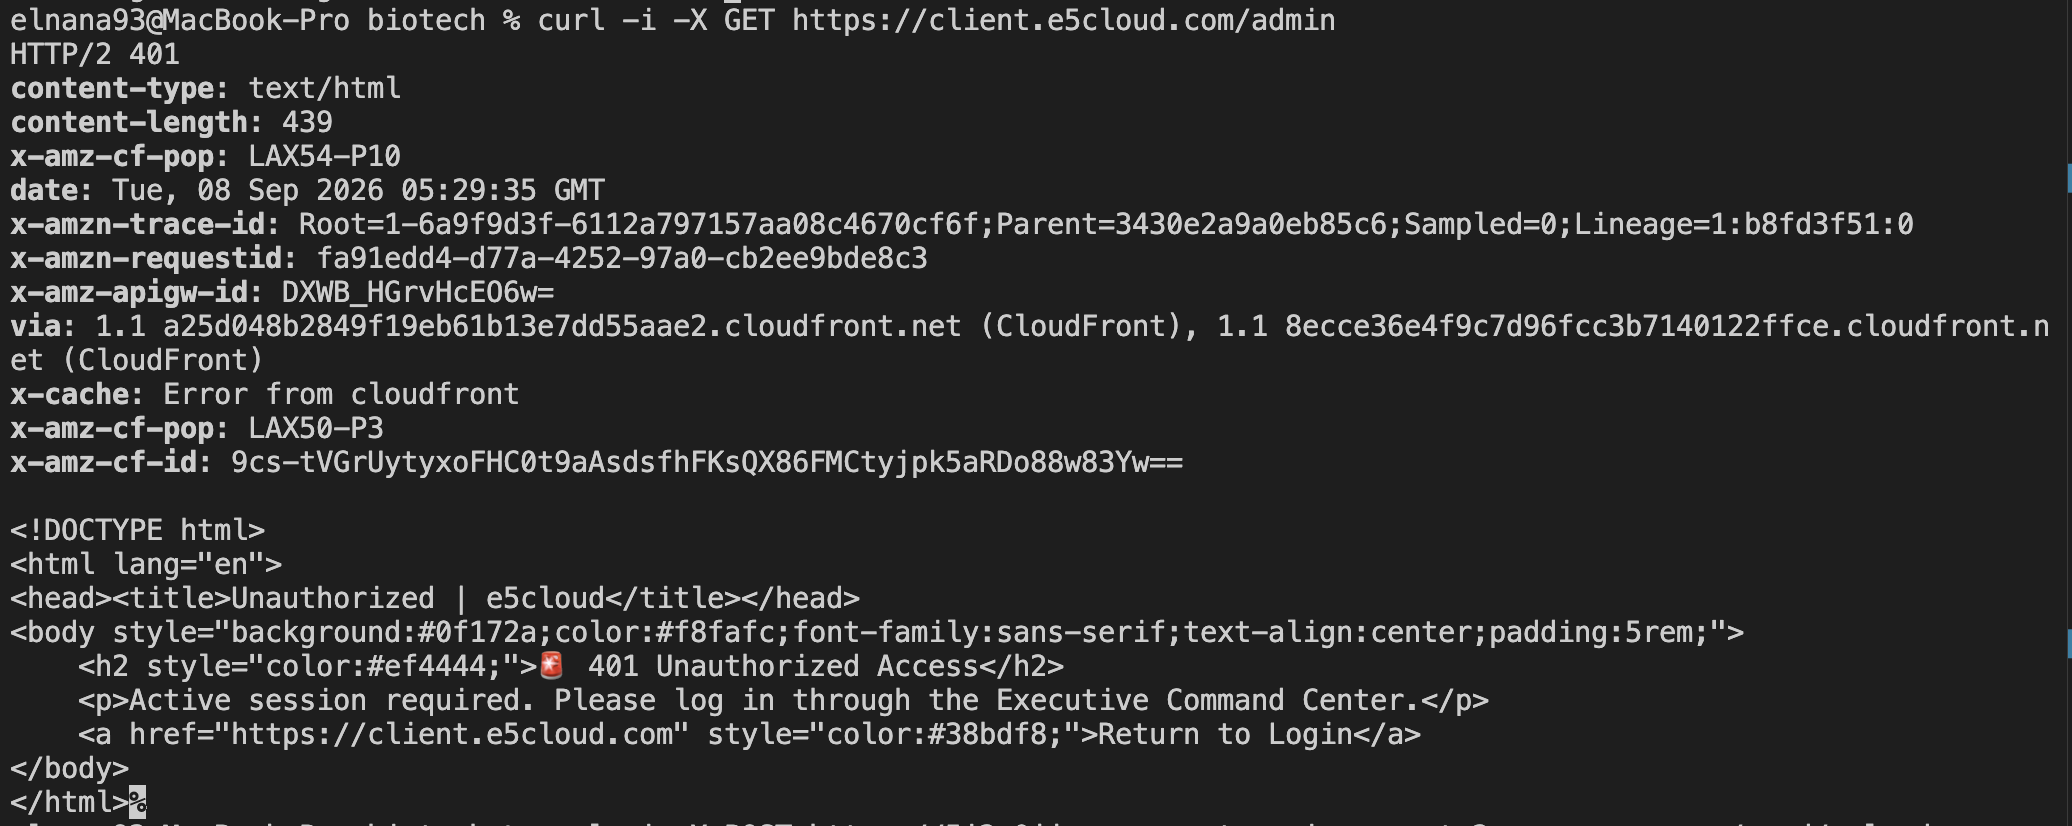
Validates perimeter enforcement on restricted management planes, confirming that unauthorized administrative navigation triggers a secure HTTP/2 401 Unauthorized challenge and redirect response.
API Gateway Production Stage Direct Invocation Test:
Tests raw serverless gateway endpoints via curl -i -X POST https://5i2v0jjzne.execute-api.us-west-2.amazonaws.com/prod/upload.
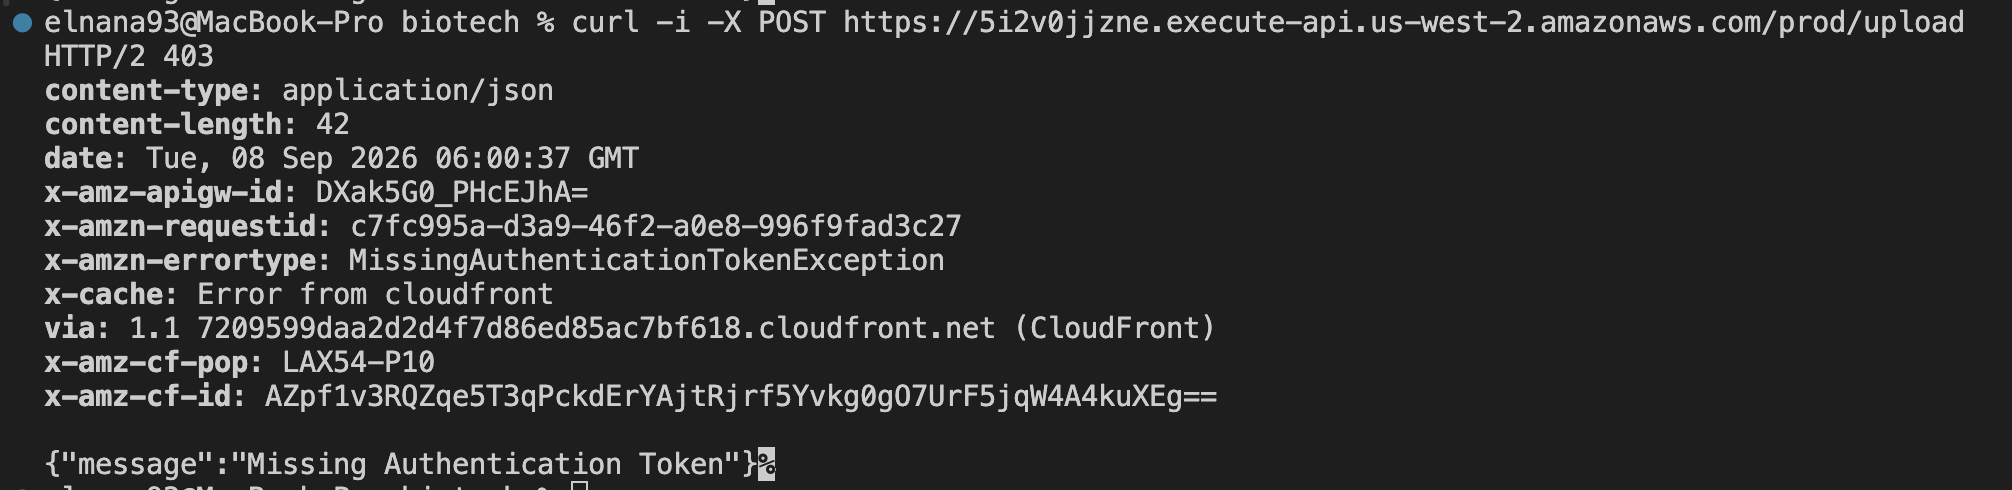
Tests raw serverless gateway endpoints to ensure that core infrastructure is protected against unauthorized compute triggers and unbilled execution cycles, returning an immediate HTTP/2 403 Forbidden response.