🛡️ System Architecture & Security Controls
Real-Time Audit Logging
Powered by Amazon DynamoDB using serverless PAY_PER_REQUEST billing. Every medication administration and shift report is instantly recorded with cryptographic identifiers.
Immutable S3 Compliance Vault
Encrypted via AES256 with strict public access blocks, S3 Versioning enabled to prevent accidental deletions, and automated lifecycle rules transitioning long-term records to Glacier.
Serverless Automation
AWS Lambda container running Python 3.11, integrated securely with Telegram Bot APIs via Amazon API Gateway to deliver instant interactive shift reminders and shift logs.
📸 Live Infrastructure & Receipt Archives
Direct snapshots of live infrastructure workflows, AWS console states, and uploaded physical compliance/expense logs (Click any photo to zoom):
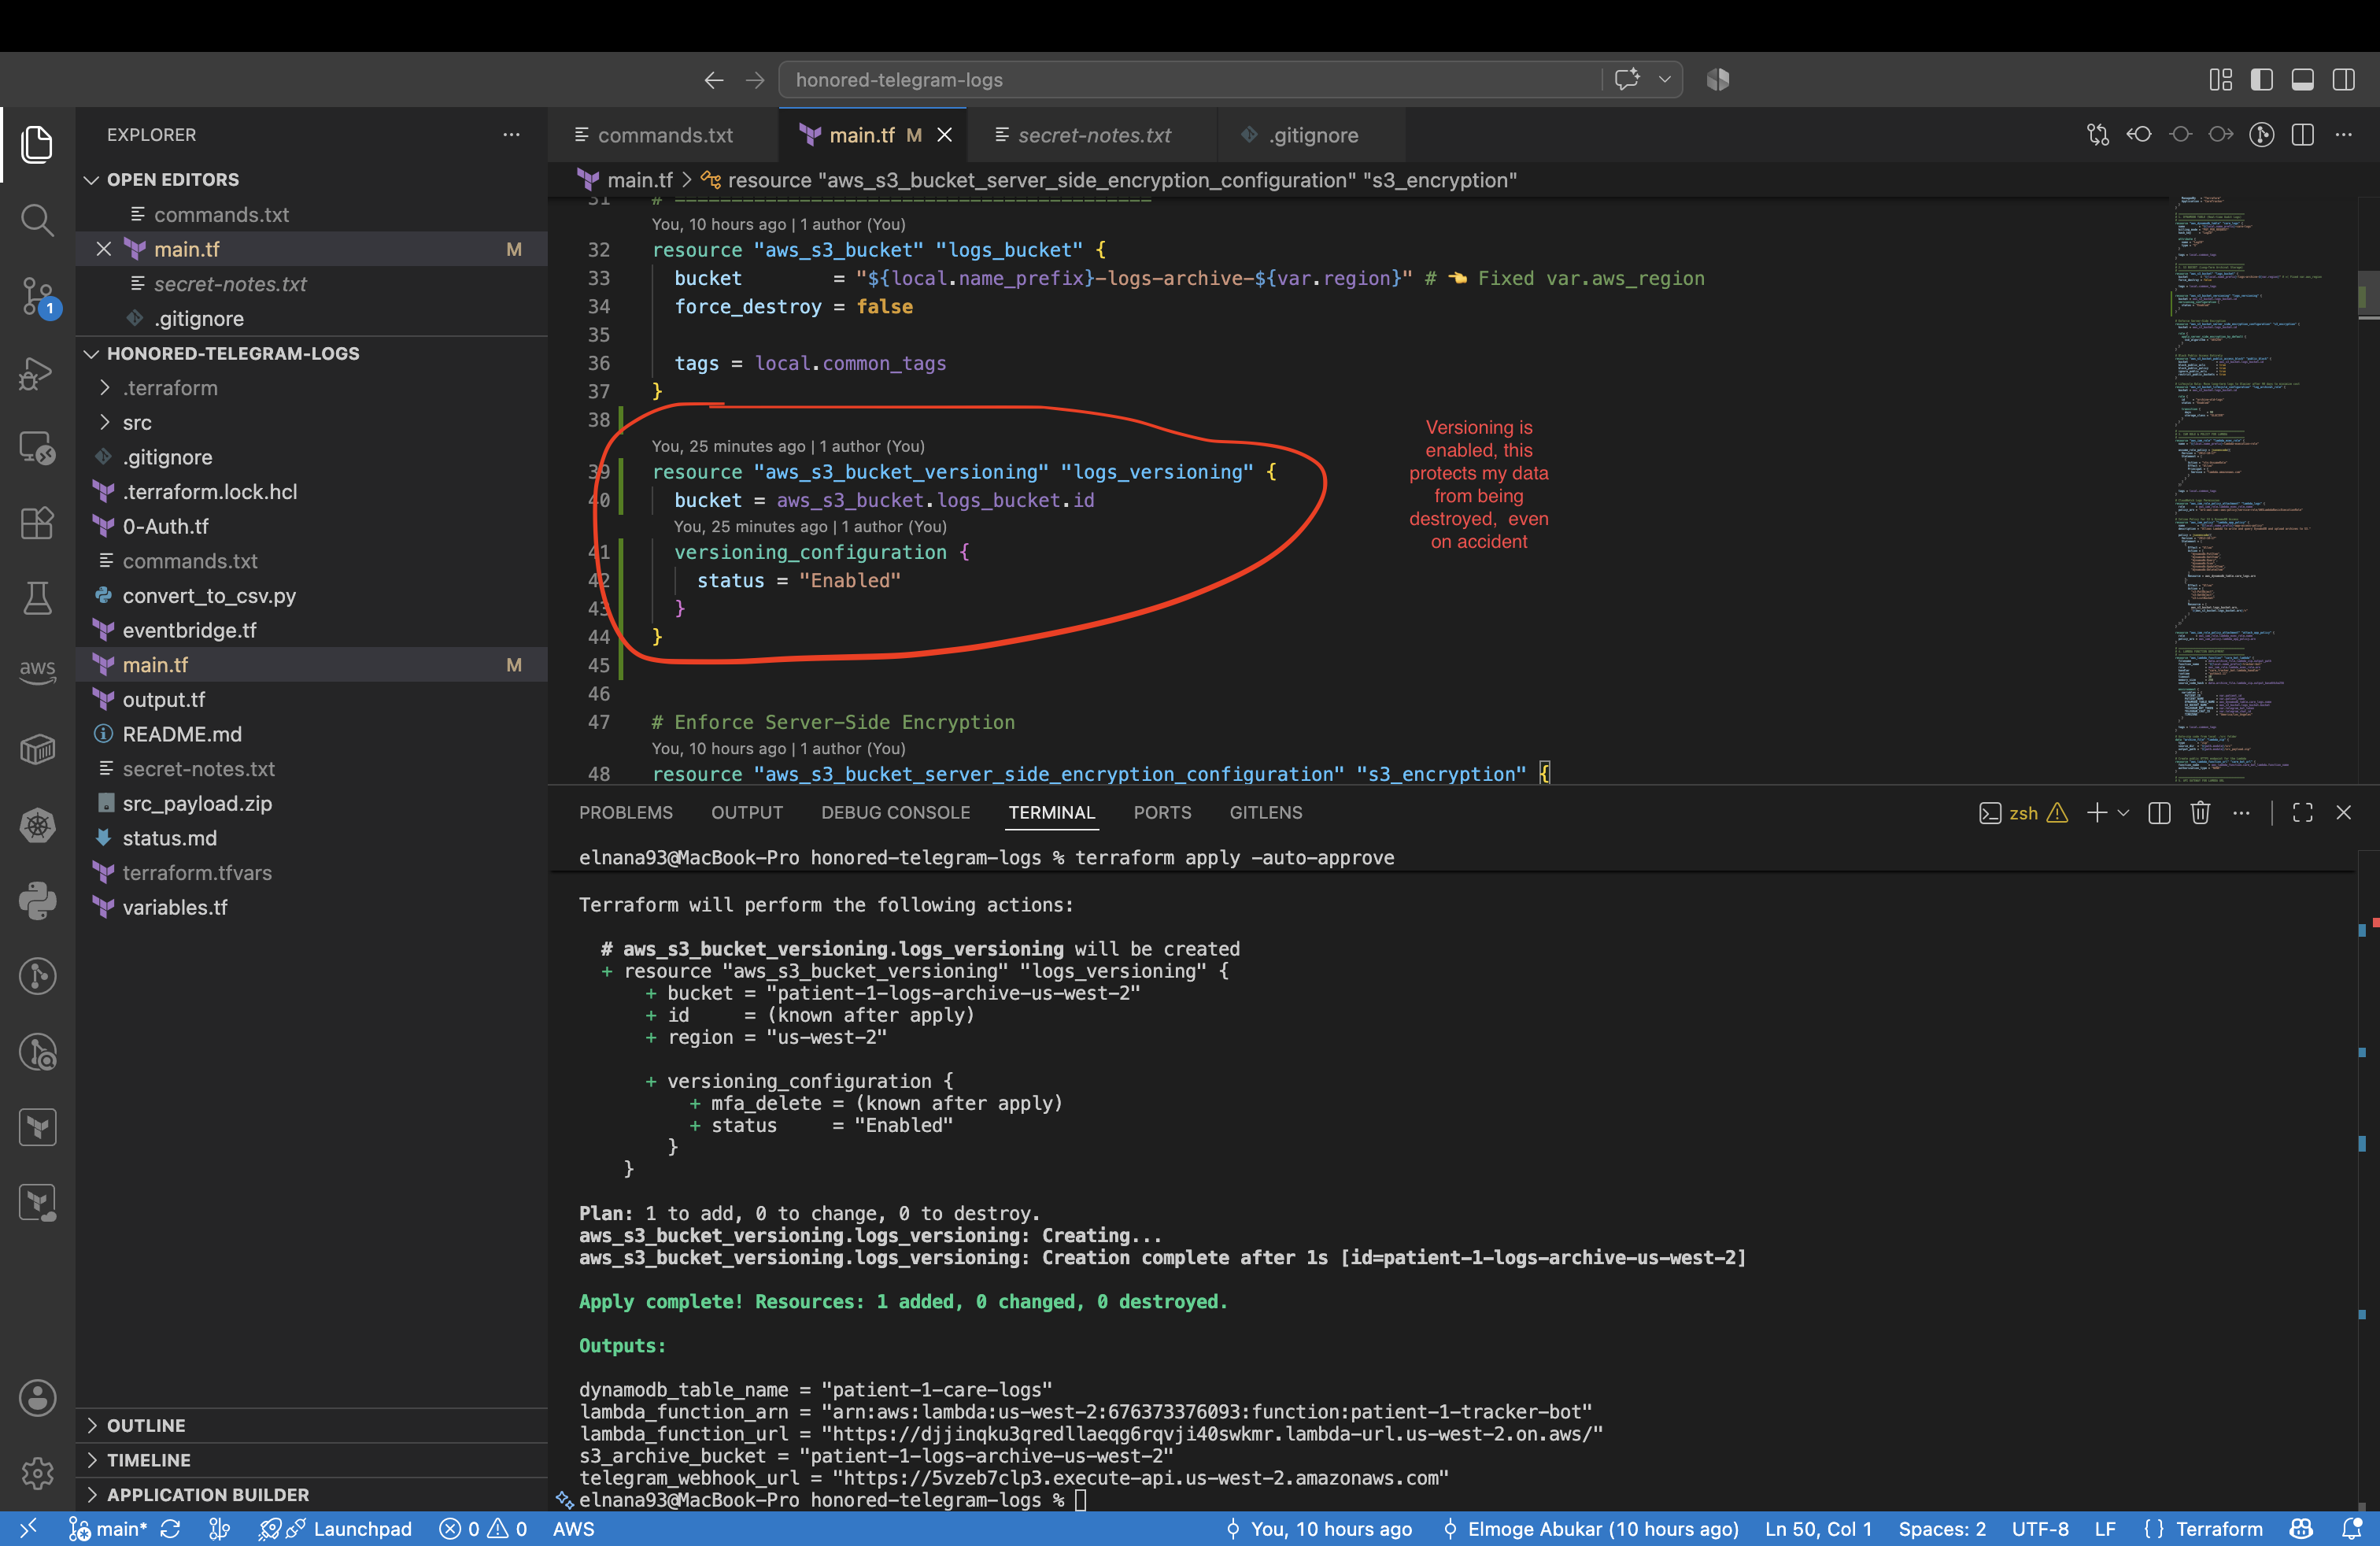
Setting force_destroy = false only prevents Terraform from deleting your S3 bucket during a destroy command while files are still inside, leaving your data vulnerable to manual or accidental deletions. Enabling S3 versioning ensures that every deleted or overwritten file is safely preserved behind the scenes, making your data fully recoverable.
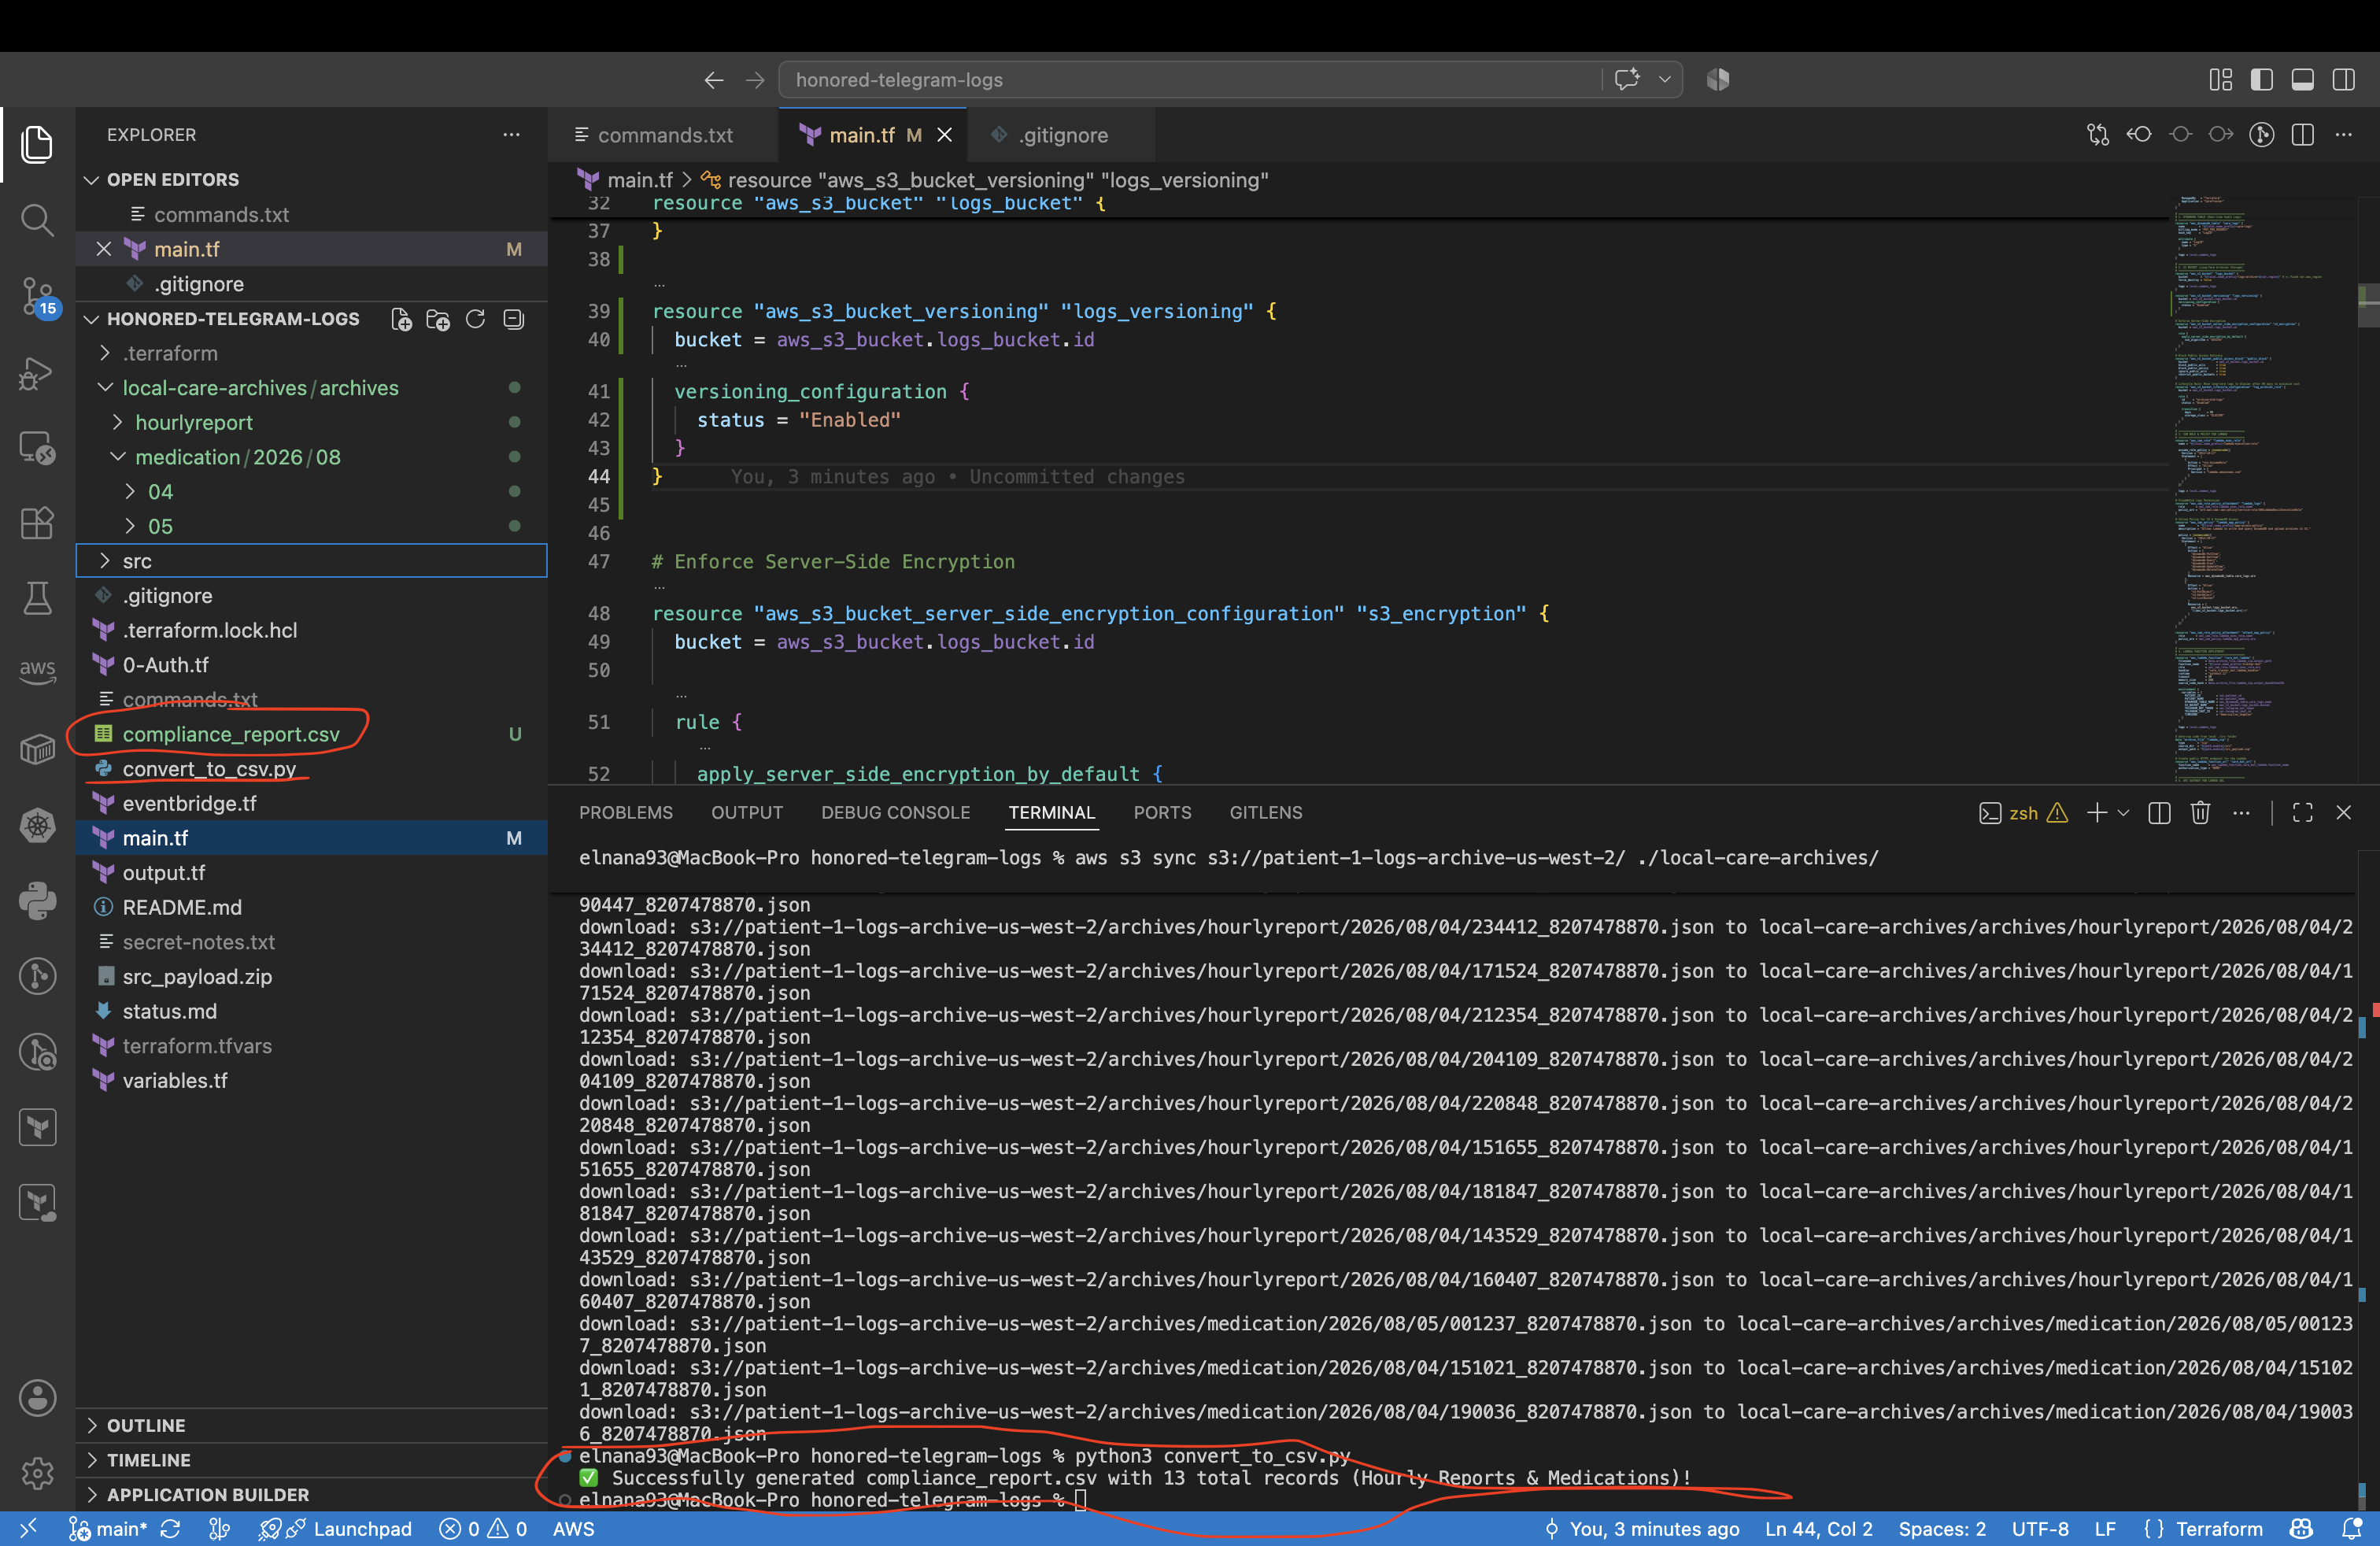
We use a simple command to pull raw, unedited logs and reports straight from your secure AWS S3 cloud storage folder down to your local computer. Then, a quick Python script processes those files and instantly converts them into a clean, organized spreadsheet.
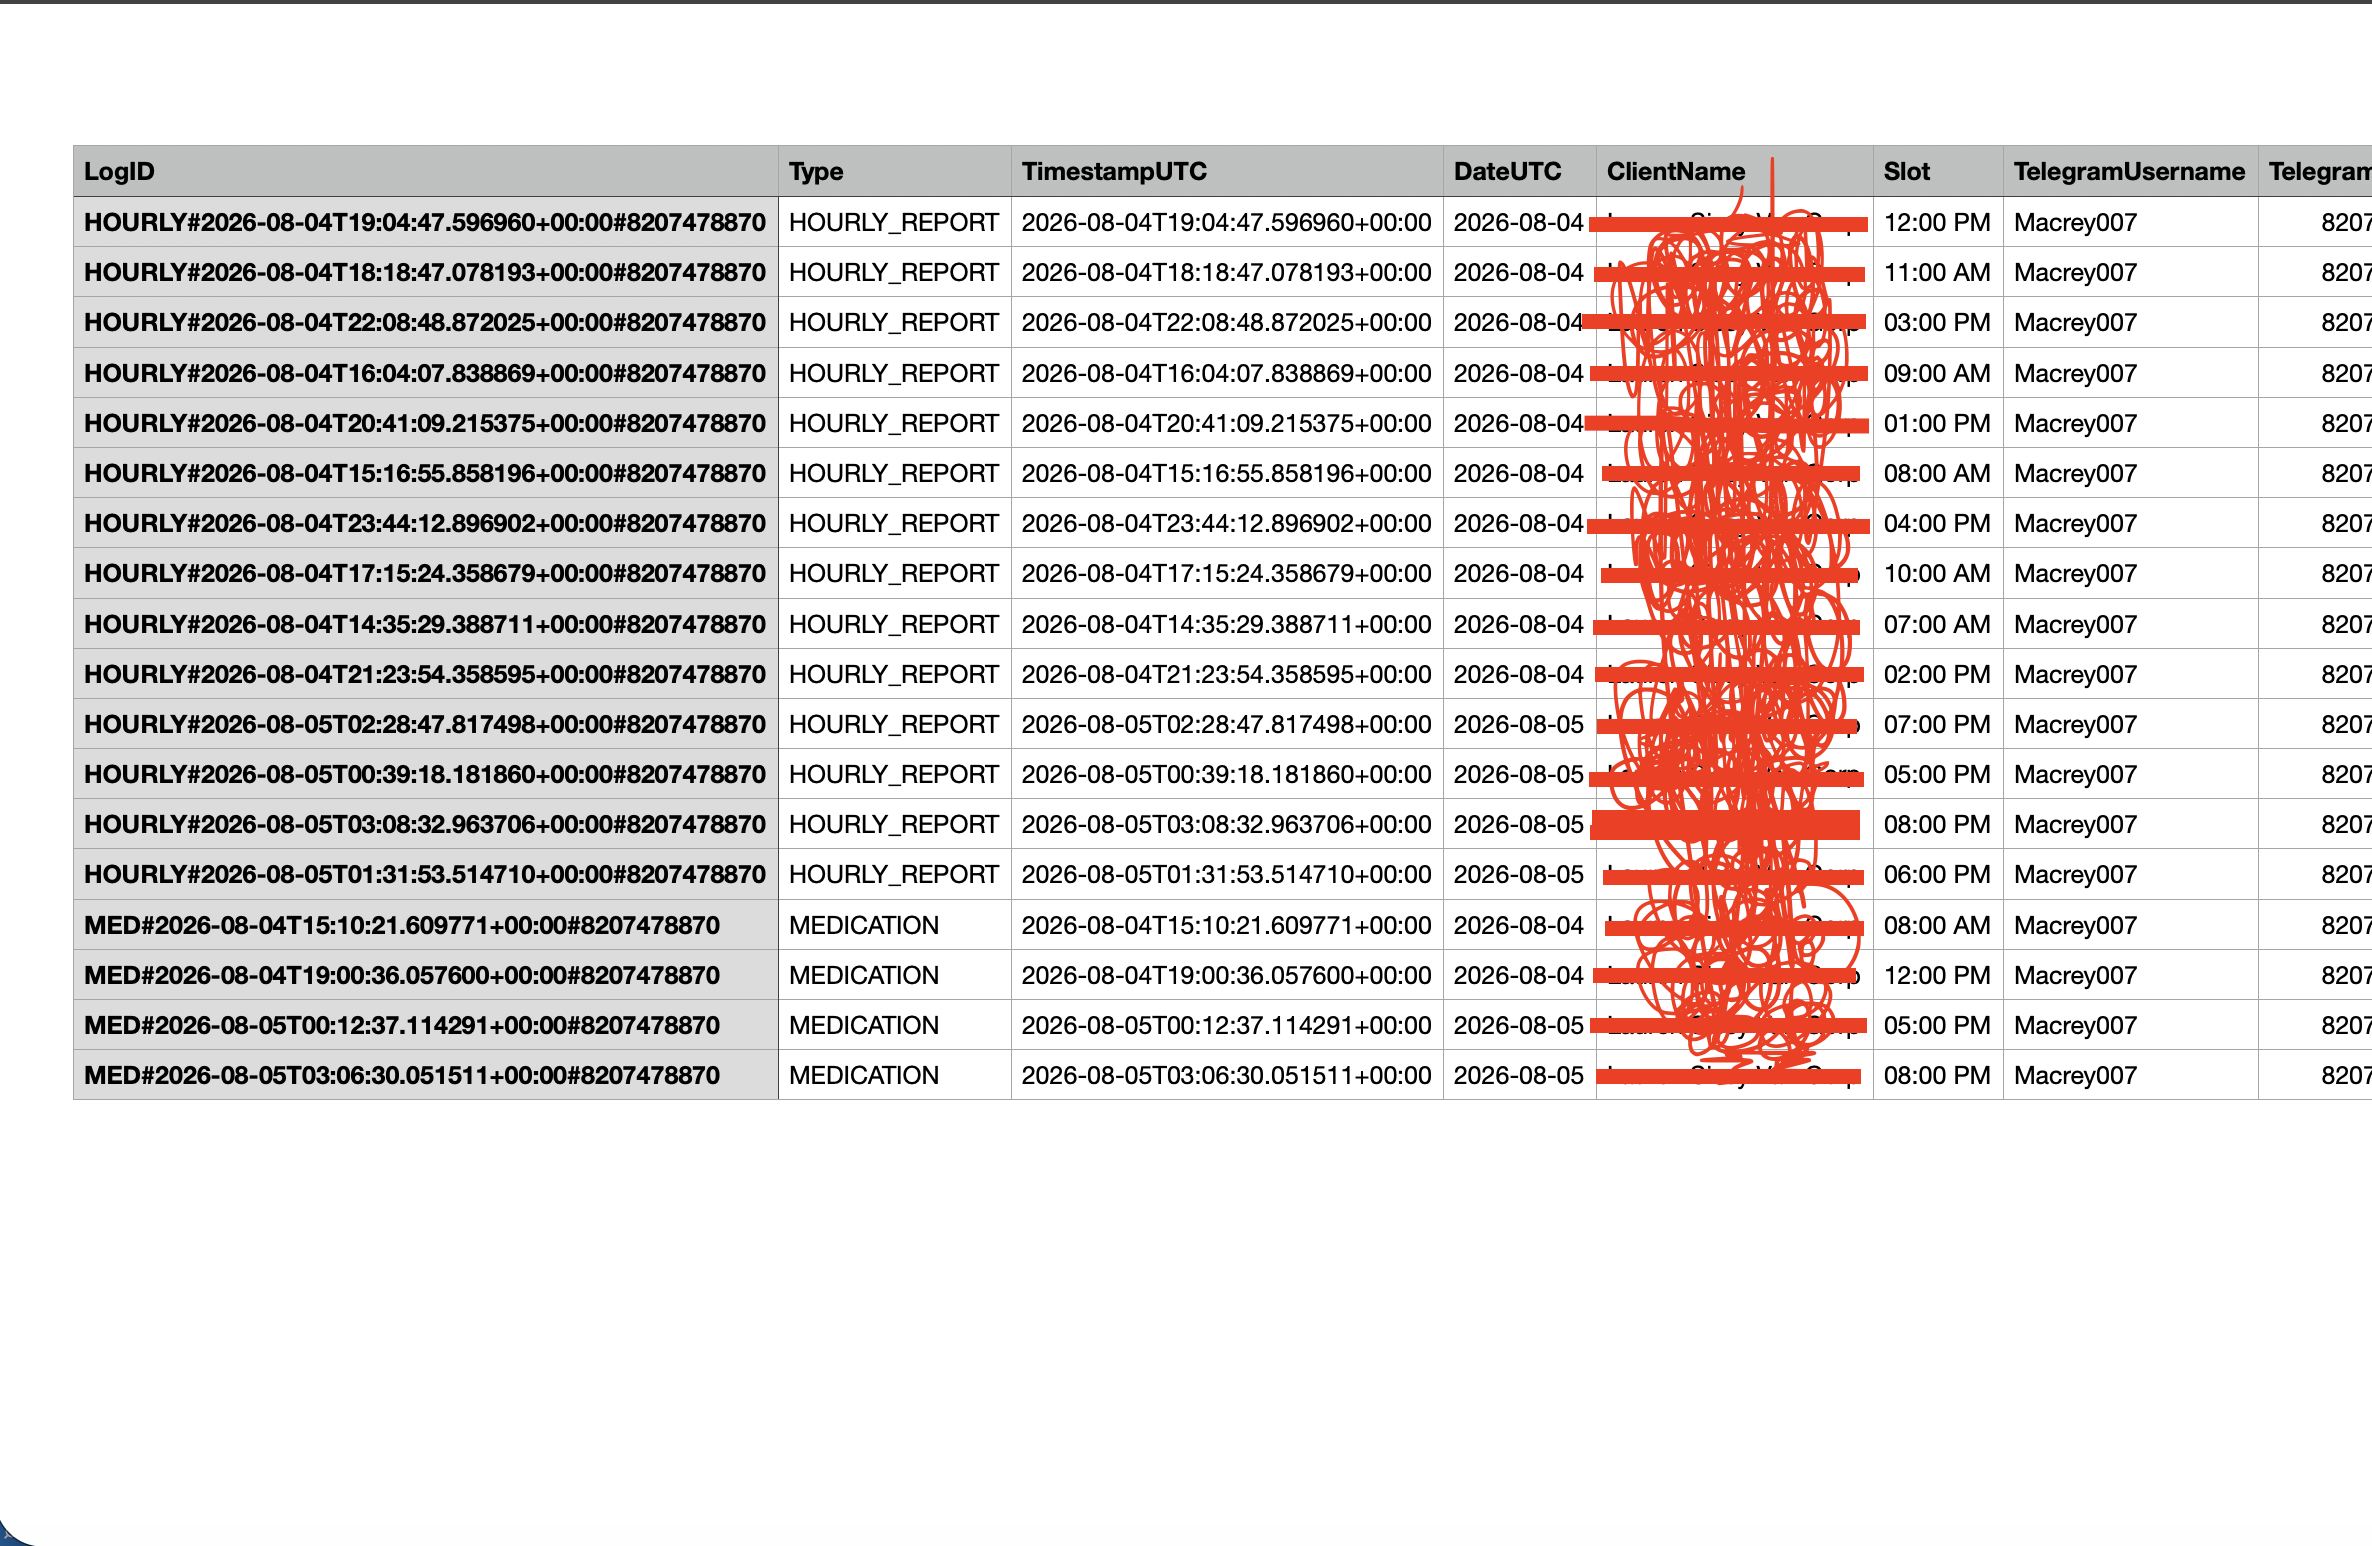
Here is the organized CSV data straight from the command, structured, fully auditable, and compliant for seamless reporting and review.
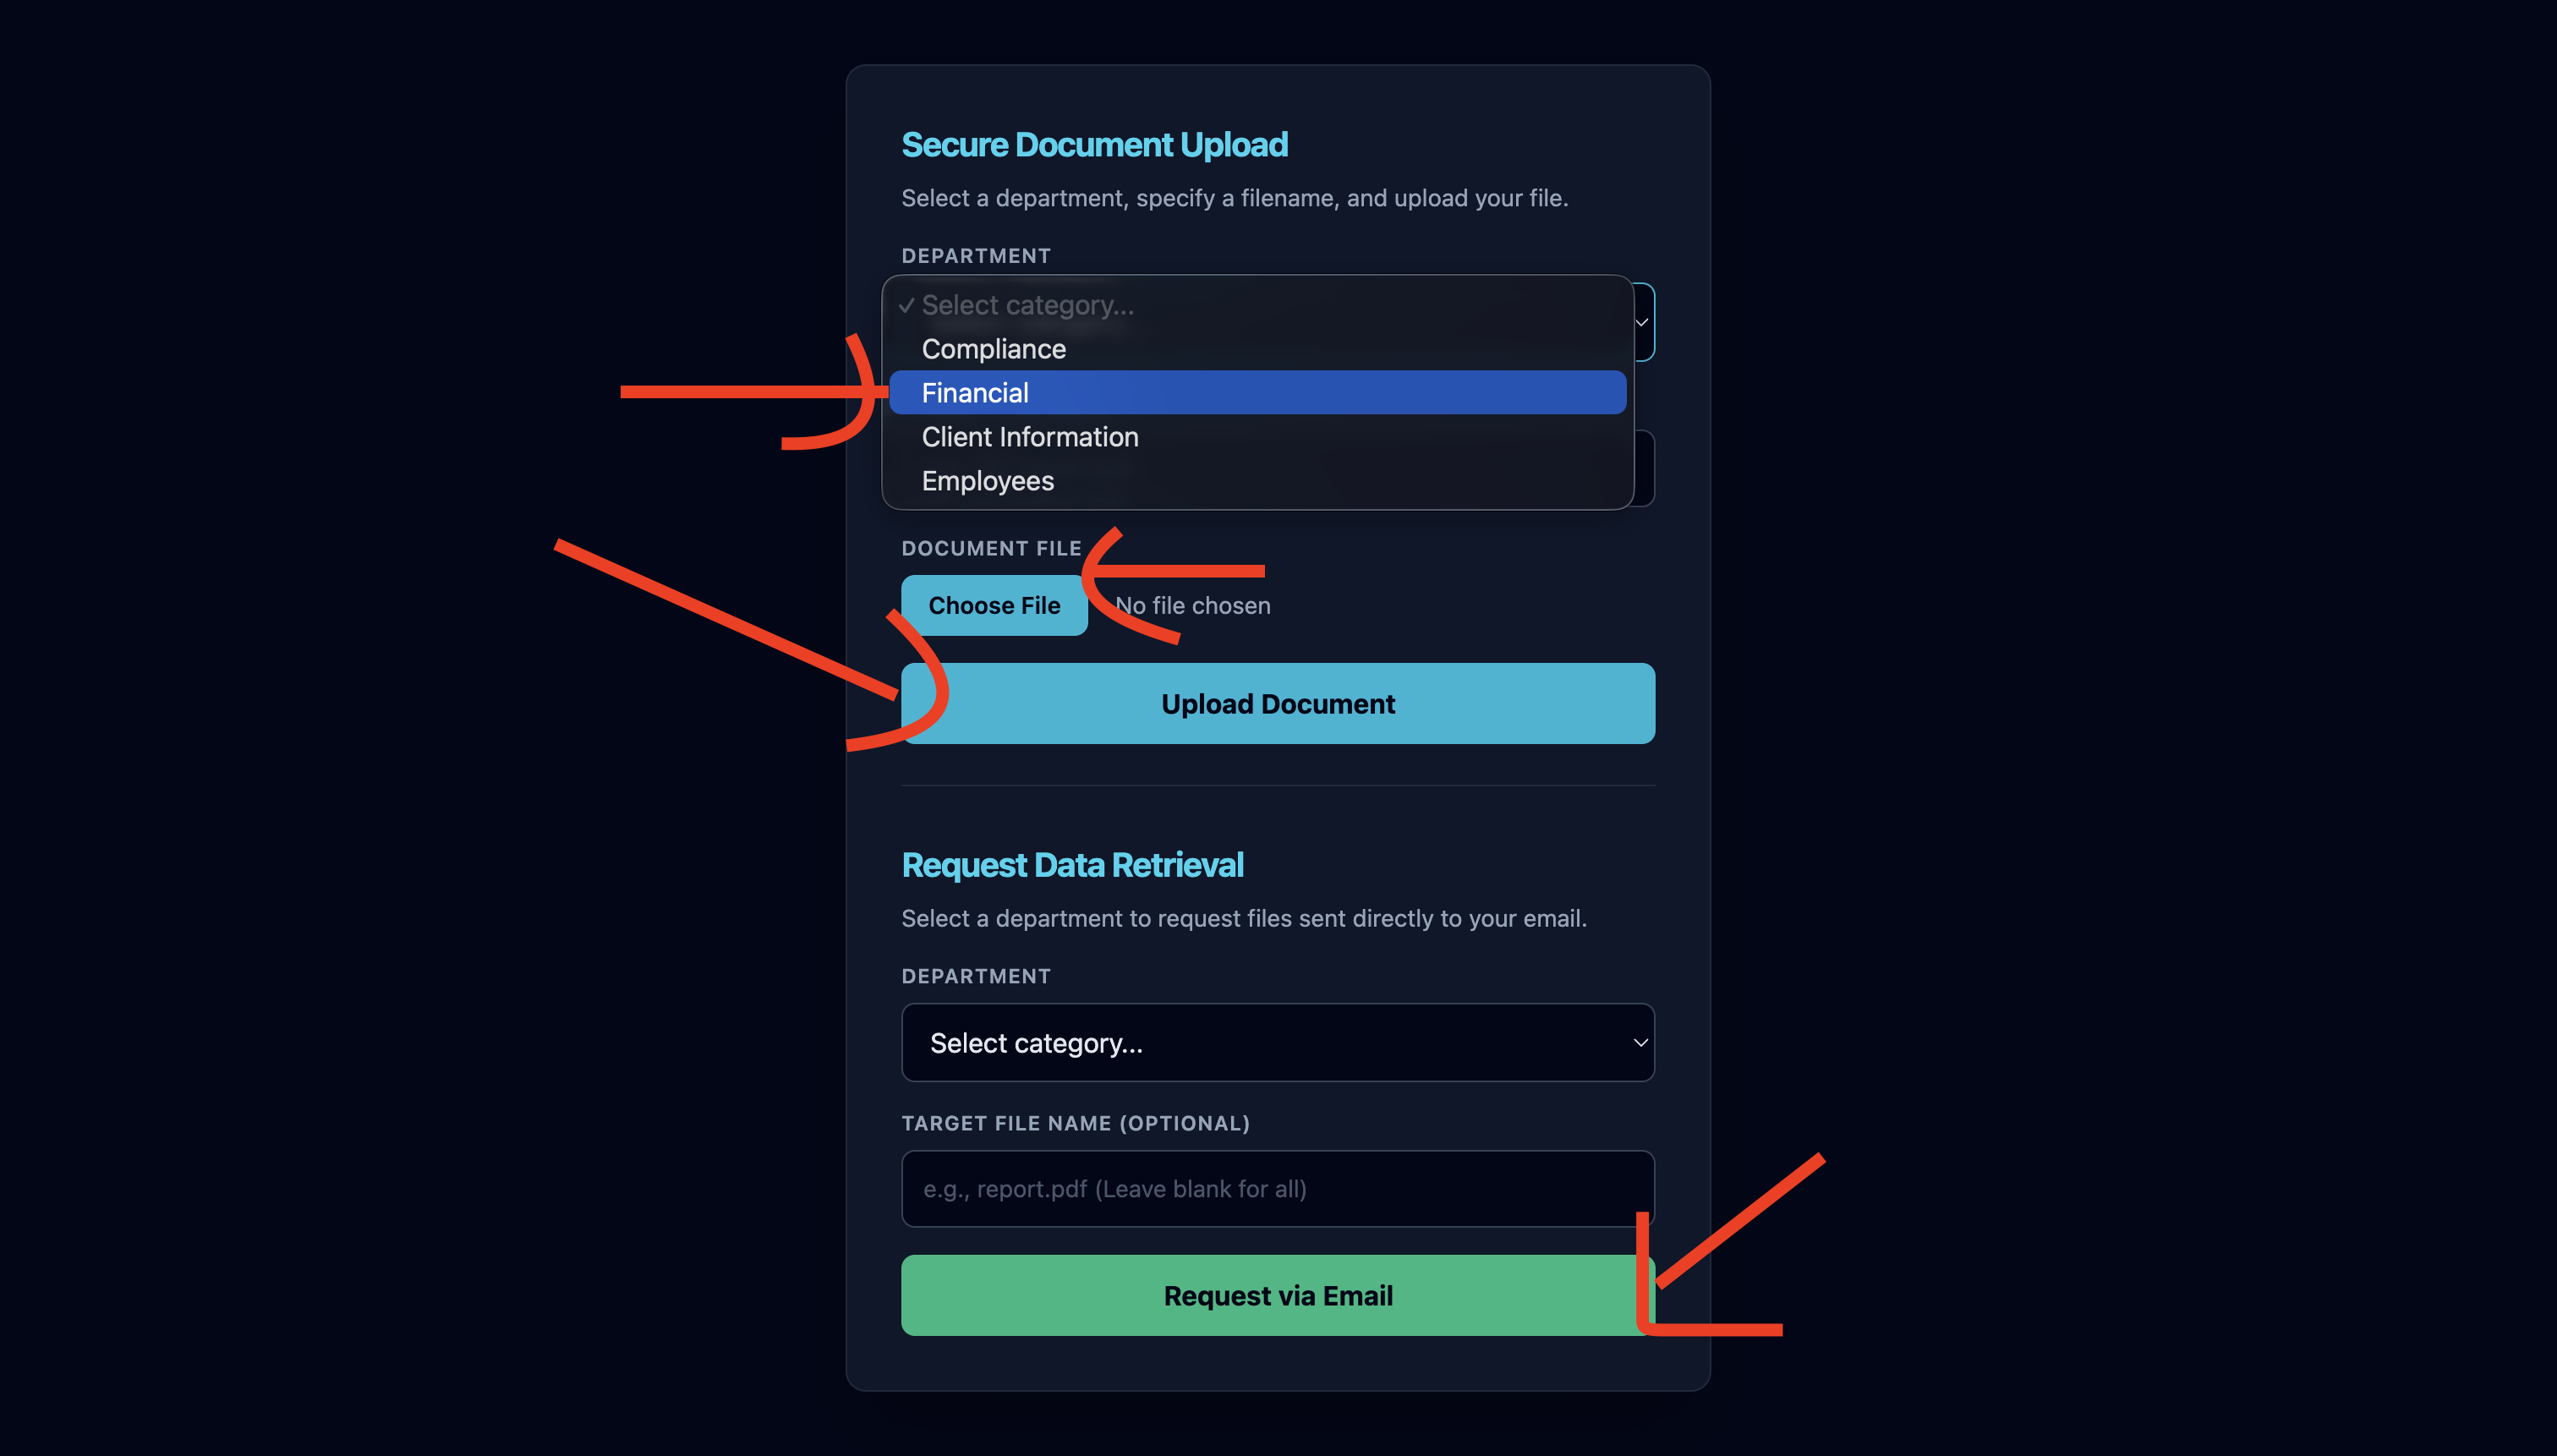
Secure interface enabling seamless data ingestion and cryptographic storage directly within an isolated AWS S3 bucket architecture.
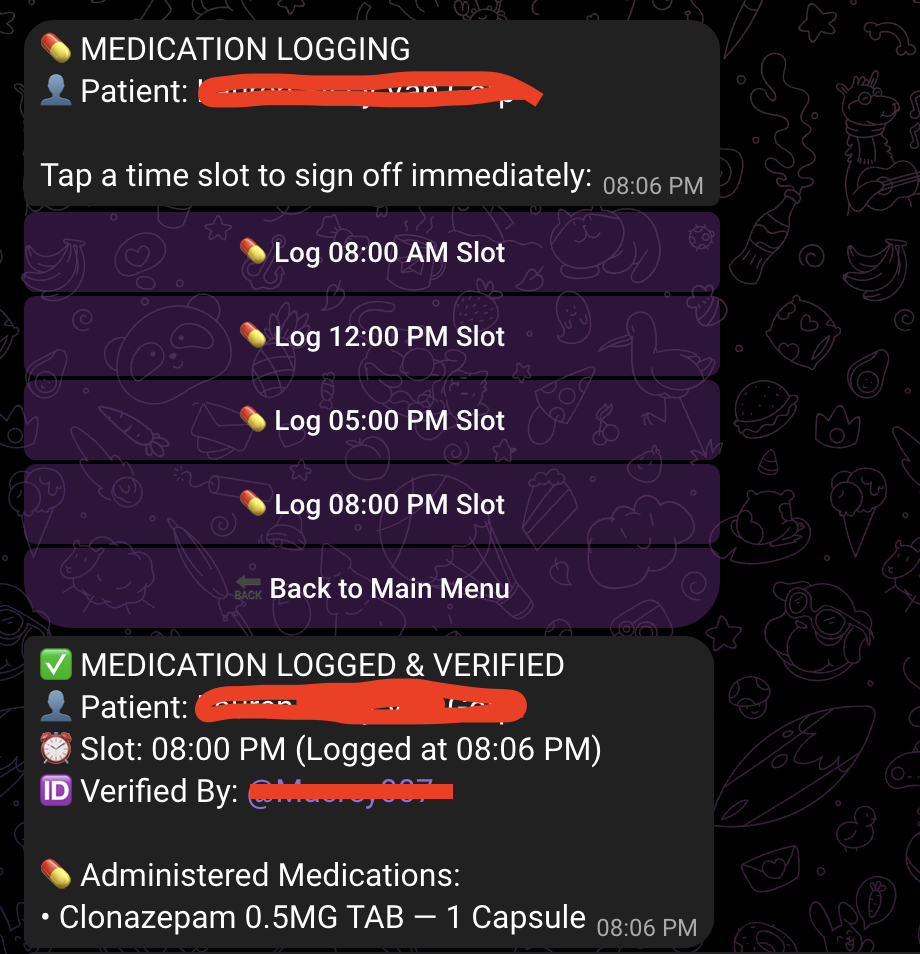
Telegram Bot Interface that logs shift activities and medication administrations.
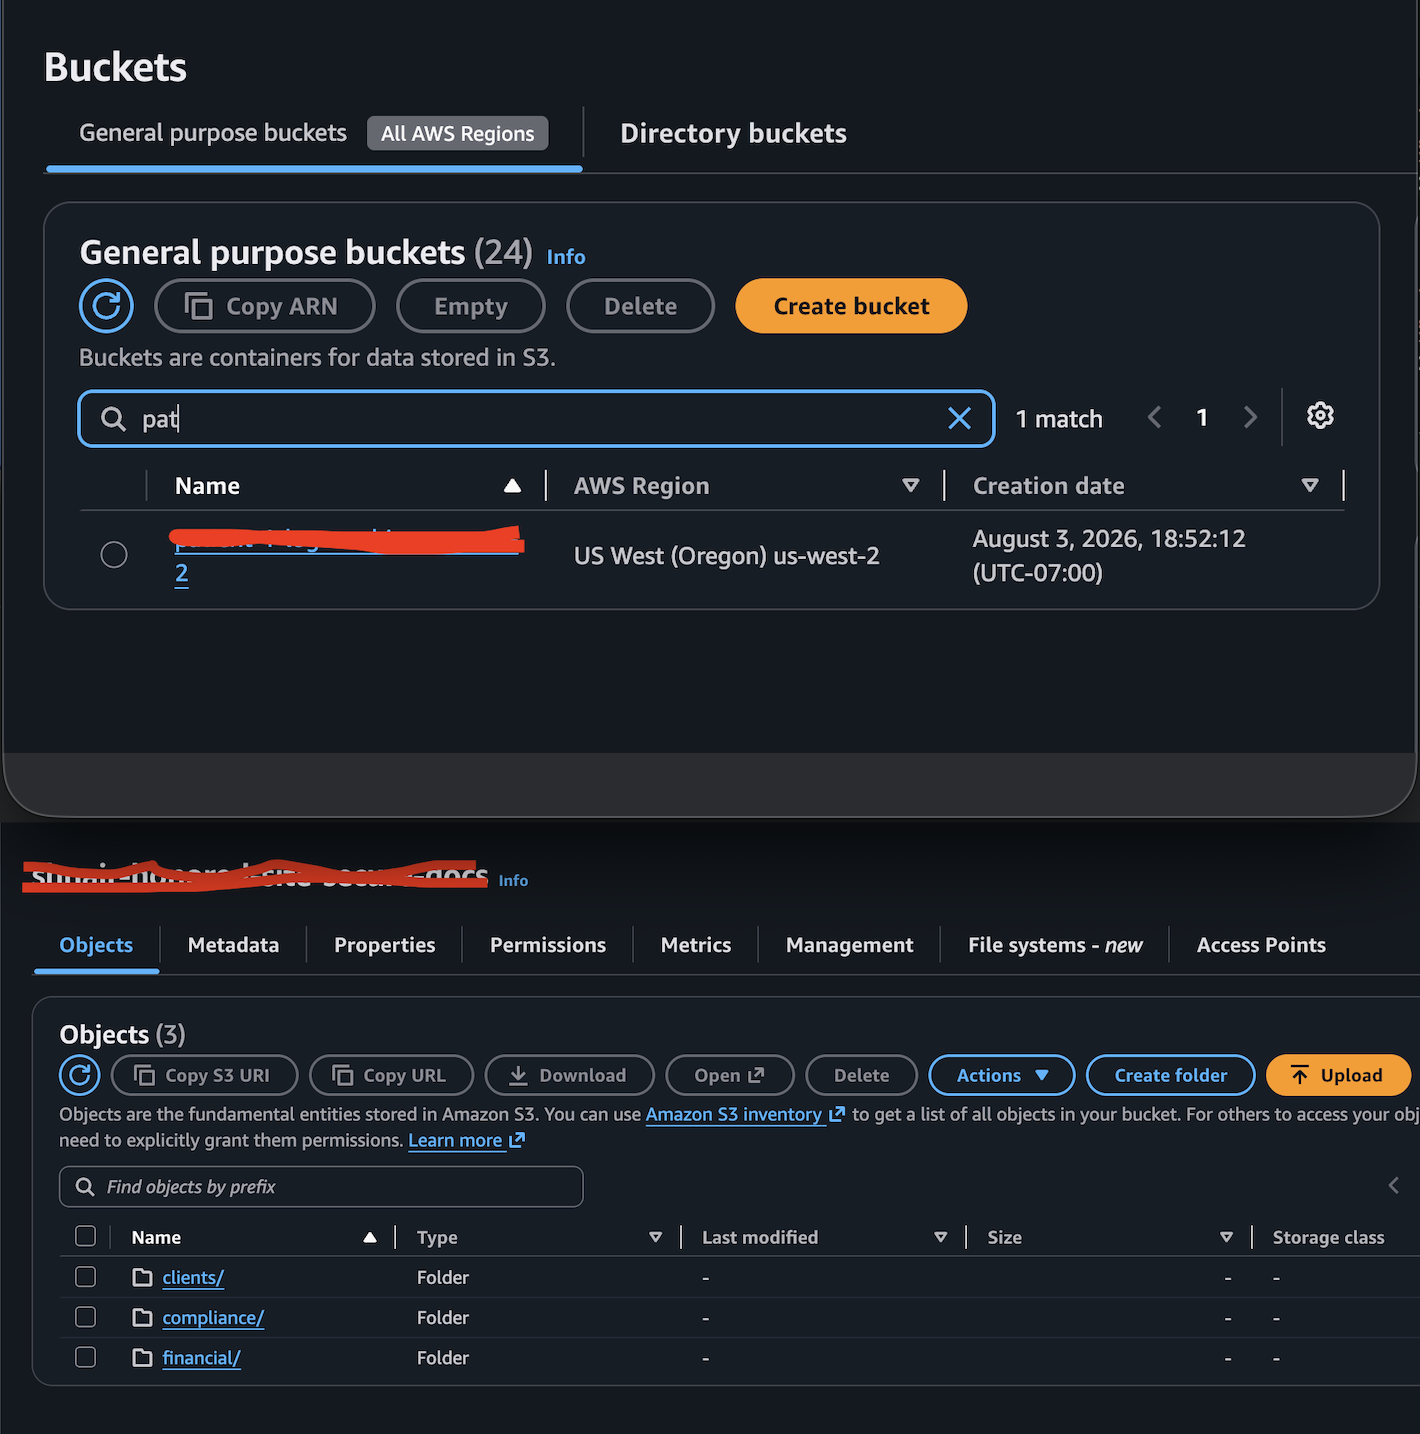
Data secured in a compliant S3 bucket with versioning enabled.